
Graylog Alert Triage Automation — AI Tickets + FortiGate Auto-Block (n8n)
What if every Graylog alert arrived as a fully-written incident ticket enriched, analyzed, and ready to action before your analyst even opened their laptop?
That's not a fantasy. That's what this workflow delivers. You plug it in once, and from that moment forward, your SOC operates like a team twice its size.
The transformation:
- Before: Alerts pile up in Graylog. Tier-1 analysts burn hours copy-pasting IPs into VirusTotal, digging through logs, writing tickets by hand, and escalating only after the damage is done.
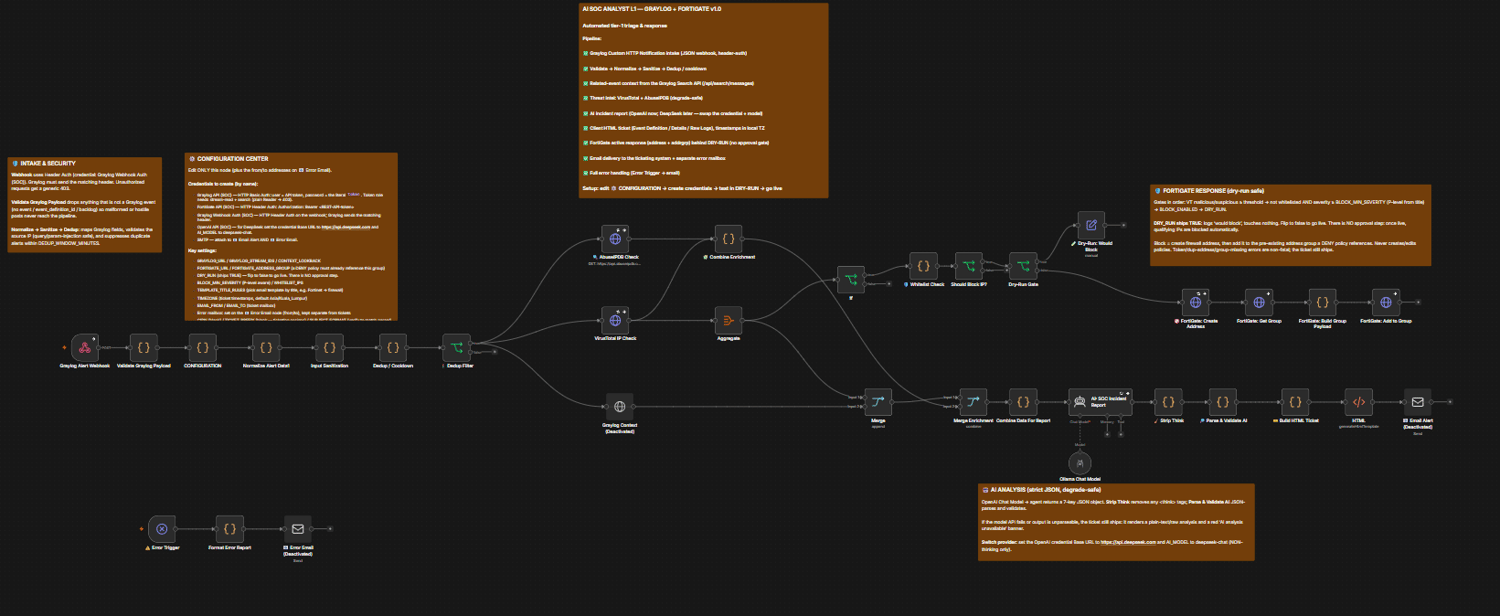
- After: Graylog fires an alert. Seconds later, a formatted ticket lands in your inbox with VirusTotal and AbuseIPDB verdicts, related log context, an AI-written analysis, a recommended action, and if warranted the malicious IP already blocked at the firewall. Your analyst reviews, approves, and moves on. Or doesn't even need to.
Every alert triaged, enriched, documented, and actioned automatically so your team only touches what actually matters.
"This sounds great, but will it actually work in Your environment?"
Yes. And here's why you can believe it:
It ships safe.
- Blocking runs in dry-run mode by default. You see exactly what would have been blocked before a single packet is dropped. No surprises. No outages. No "the automation blocked our CEO."
- Every enrichment source (VirusTotal, AbuseIPDB, Graylog Search) retries on failure and degrades gracefully. If one is down, the ticket still goes out—with a banner telling you what was missing.
- If the AI fails or returns garbage, the ticket still goes out with raw analysis and a clear warning. No silent failures.
- If the ticket email fails, it retries three times, then fires an error email to a separate ops mailbox. An alert is never lost silently.
It's built for real SOCs, not demos.
- Webhook is header-authenticated. Malformed or hostile posts get dropped before they reach the pipeline.
- Log lines are HTML-escaped. Attacker-controlled input can't inject scripts into your ticketing system.
- Whitelist support means your own ranges are never touched.
- Duplicate suppression stops the same alert from flooding your queue.
What do you have to give up to get this?
What you don't have to do:
- ❌ Hire another Tier-1 analyst
- ❌ Build a custom SOAR playbook from scratch
- ❌ Pay for a enterprise automation platform
- ❌ Write code (the workflow is pre-built; you configure, you don't develop)
- ❌ Change your ticketing system (it emails a formatted ticket; your existing parser handles it)
- ❌ Rip and replace your SIEM (it works with Graylog, not instead of it)
What you do need:
- ✅ A self-hosted n8n instance (you probably already have one, or can spin one up in minutes)
- ✅ Graylog with API access (you have this)
- ✅ API keys for VirusTotal, AbuseIPDB, and OpenAI (free tiers work)
- ✅ An SMTP account (you have this)
- ✅ Optional: FortiGate REST API access for automated blocking
About an 30 minutes of setup. A week of dry-run observation. The willingness to let a machine write your first-draft tickets and the discipline to review them until you trust them.
That's it. No new headcount. No new platform. No six-month implementation.
Why this? Why now?
Because Tier-1 burnout is real, and it's expensive.
Your best analysts didn't join your SOC to copy-paste IPs into VirusTotal. They joined to hunt threats, not to be human API gateways. Every hour they spend on manual triage is an hour they're not spending on the advanced work that actually protects your business.
And because the tools are finally good enough.
- LLMs can now write structured, useful incident reports—not hallucinated garbage, but JSON with title, description, analysis, action, category, and severity.
- VirusTotal and AbuseIPDB have free tiers that cover most SOC volumes.
- n8n gives you enterprise-grade automation without enterprise-grade pricing.
- Graylog's API gives you the context you need programmatically.
This isn't "move fast and break things." This is "automate the boring stuff, keep the human in the loop for the scary stuff, and sleep better at night."
Need help?
Want to customize or deploy it for you? Get deployment & customization
Guarantee
If the workflow does not import or work as described, contact me and I will fix it or refund you.