
AI SOC Analyst L1 - For Wazuh SIEM + Guide
On Sale
$49.99
$49.99
Your Wazuh alerts get investigated and written up before you open your laptop.
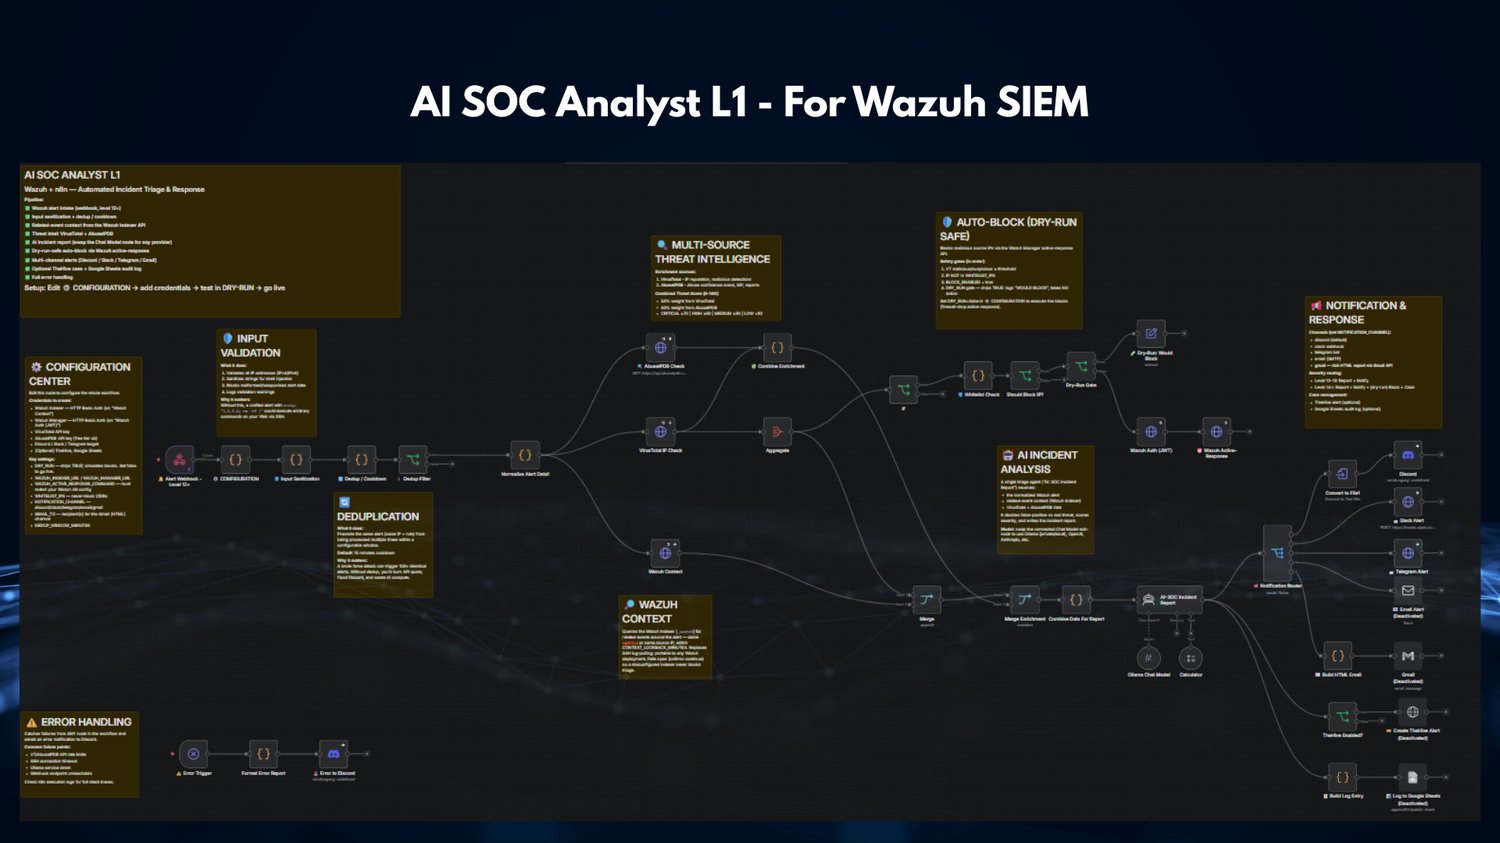
This n8n workflow automates the tier-1 alert investigation process. It gets context from Wazuh, checks IPs with VirusTotal and AbuseIPDB, uses local AI to analyze the alert, and sends a ready-to-read incident report to your preferred channel.
No SSH. No manual investigation. Your data stays on your infrastructure.
What it does
- Removes duplicates — Groups repeated alerts from the same attacker instead of creating hundreds of reports.
- Gets the full context — Searches your Wazuh Indexer for related activity.
- Enriches IPs — Combines VirusTotal and AbuseIPDB into a single threat score.
- AI triage — Gives you a verdict, false-positive assessment, MITRE technique, and recommended actions.
- Sends reports automatically — Discord, Slack, Telegram, email, or any combination.
- Optional auto-blocking — Wazuh Active Response can block malicious IPs behind multiple safety checks.
- Local AI — Ollama runs on your hardware, keeping alerts and logs away from cloud AI.
Built with safety in mind
- Dry-run enabled by default
- Multiple checks required before blocking an IP
- Built-in IP and CIDR whitelist
- No SSH access required
- Uses Wazuh APIs
- Workflow errors are reported instead of failing silently
How it works
- Import the workflow into n8n.
- Configure the Wazuh URLs in the CONFIGURATION node.
- Add your credentials.
- Connect the Wazuh webhook.
- Send a test alert and receive your first report.
Setup takes about 15 minutes.
What's included
- 49-node import-ready n8n workflow
- 3 test alerts
- 3 HTML report designs
- Sample incident report
- Complete setup guide
- Full configuration reference
- Field reference for customization
- Single-organization commercial license
Requirements
- n8n v1.x+
- Wazuh 4.x
- Ollama or another supported AI model
- VirusTotal API key
- AbuseIPDB API key
- Discord, Slack, Telegram, SMTP, or Gmail
Free API tiers are enough to get started.
$49.99 — One time
No subscription. No per-alert fees. No per-seat fees.
You buy the workflow and run it on your own infrastructure.
Built for
SOC engineers · MSPs · Security consultants · One-person security teams · Wazuh users
Need help?
Want help deploying or customizing it? Get deployment & customization
Guarantee
Try it for 7 days. If we can't get it working with your setup, you'll get a full refund.