
Threat Hunter: AI Threat Hunting for Wazuh
On Sale
$67.99
$67.99
Find the attackers who got past your alerts
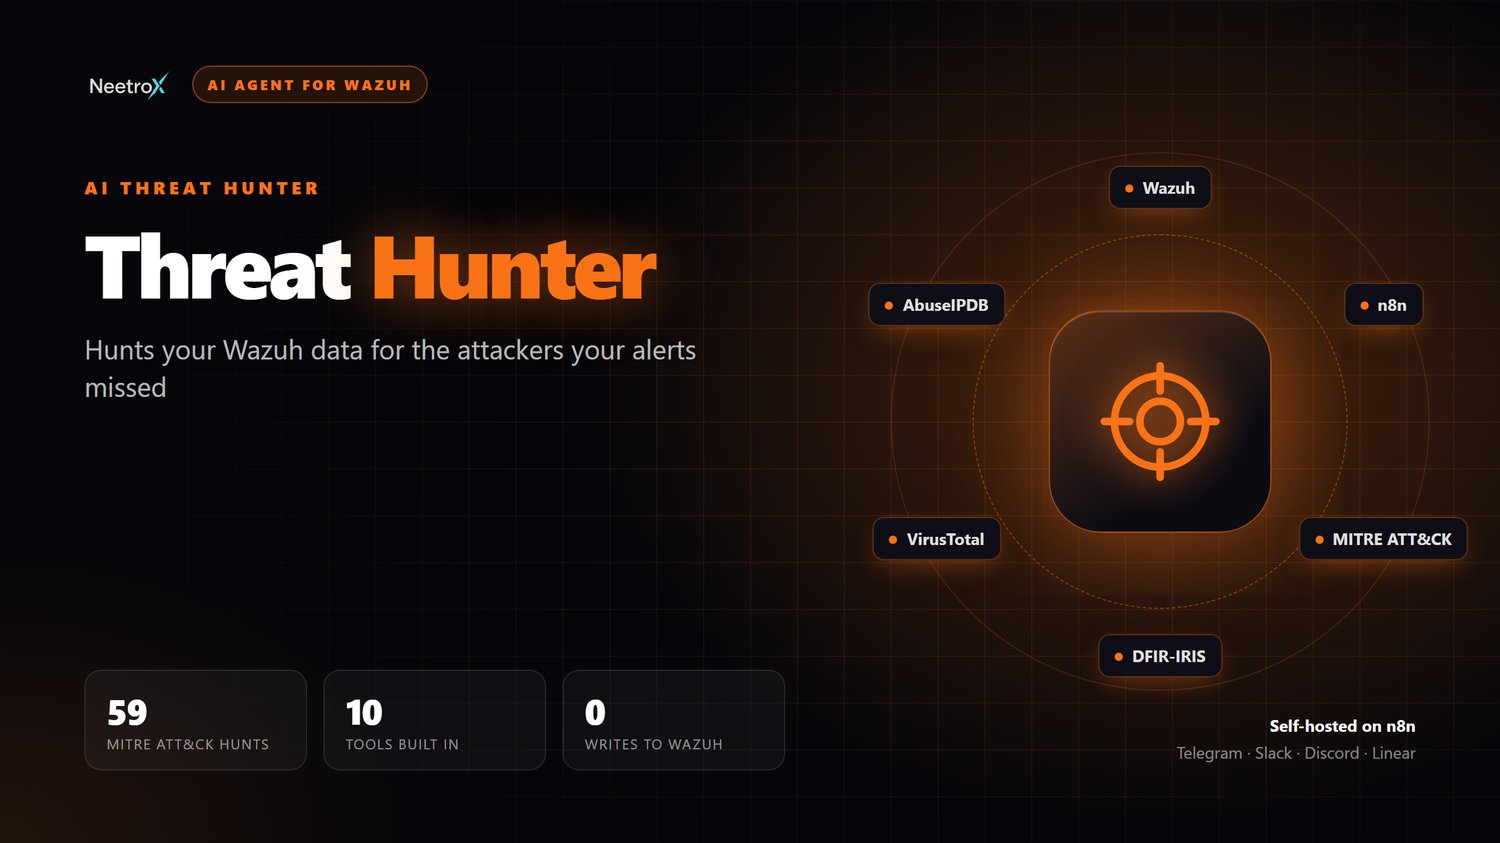
Ask in plain English. It plans the hunt from 59 MITRE ATT&CK hunts, runs it on your Wazuh data, triages what comes back and records every real lead as a finding.
Alerts catch what rules already know. Attackers live in the gaps
Today: you wait for a rule to fire
- A valid login at a strange hour raises nothing
- Hunting needs query skills and senior time
- Nobody knows which hunts are blind
With the Threat Hunter: you go looking
- Hunt in plain English, by hypothesis, tactic or entity
- New users, binaries and changed files surfaced every week
- A coverage check says which hunts can fire and which are blind
A senior threat hunter in your team chat
- 59-hunt ATT&CK library: 30 Windows, 18 Linux and 11 cross-platform hunts, each with a hypothesis, a threshold, a triage hint and false-positive notes
- Many hunts at once: One batch query for any set of hunts, a whole tactic, this week's rotation or all 59
- Ad-hoc hunts: Typed filters on rule, technique, host, IP, user, process, command line, file, hash or domain, with optional stacking
- Stack counting: Values seen for the first time this week and the rarest ones: new users, binaries, changed files and admin commands
- Entity pivots: Everything about one IP, user, host, hash or process, with first and last seen, rules, tactics and related entities
- Coverage check: Which telemetry reaches Wazuh, how many hunts can fire, which are blind and what to enable first
- Findings journal: Every real lead becomes a finding with severity, ATT&CK ids, entities and a timestamped evidence trail
- Weekly sweep: Runs a quarter of the library each week, stack-counts what is new and sends the summary and an HTML report
- DFIR-IRIS escalation: A case with the evidence, IOCs and hosts, created only after someone clicks Approve
One command, about ten minutes
- Install: Run one command on Linux, macOS or Windows. It deploys n8n too if you need it
- Connect: Add a read-only Wazuh indexer user, your chat app and an AI model key. Threat intel and DFIR-IRIS are optional
- Hunt: Ask for your first hunt. The weekly sweep runs on the day and time you pick
Hunts everything, changes nothing
- Read-only on Wazuh: The hunter never writes to Wazuh, and the weekly sweep never escalates by itself
- Facts come from tools: The model plans, triages and writes. Reports take their facts straight from the findings table
- Clean never means blind: The coverage check says when a hunt could not see the data, so silence is never mistaken for safety
- No raw queries: Chat text never reaches Wazuh as a raw query. Every filter is a typed clause
- Private IPs stay private: Internal addresses are never sent to threat-intel services
- Known-good left out: Your office and VPN IPs are excluded from every hunt
What you need
- n8n: n8n 2.34 or newer with Agents and Data Tables, or let the installer deploy it
- Wazuh: Wazuh 4.x with an indexer user that can read wazuh-alerts-*
- Chat app: Telegram, Slack, Discord or Linear. A Telegram bot takes a minute with @BotFather
- AI model: An API key from any provider in the n8n Agent model picker
- Telemetry: More data, more hunts: Windows Security auditing, Sysmon, PowerShell logging, auditd and FIM
What you get
- 10 tool workflows and the weekly sweep
- The agent with 10 hunting skills, from methodology and pivoting to persistence and write-ups
- The 59-hunt MITRE ATT&CK library
- One-command installer for Linux, macOS and Windows
- Setup guide and example conversations
- Single-organization commercial license
- 7-day money-back guarantee
Full details and a demo: neetrox.com/ai-agents/threat-hunter