
CVE Stack Monitor - CVE Alerts for Your Actual Stack
CVE Stack Monitor - Know Exactly Which CVEs Are Attacking Your Infrastructure Automatically.
Enterprise CVE intelligence platforms cost $200–$2,000/month.
This workflow does the same job - for the cost of this listing.
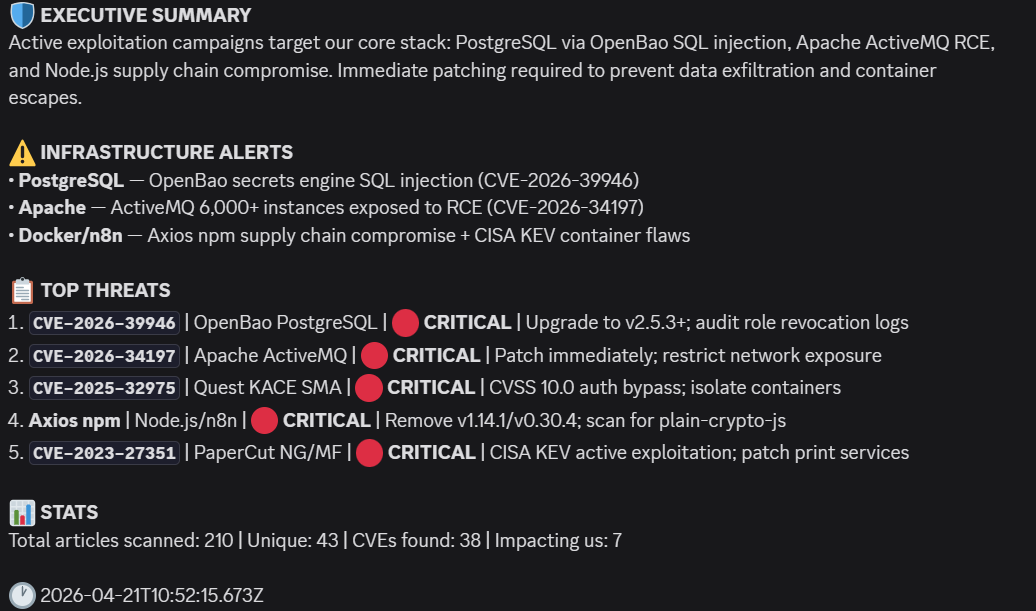
210 articles scanned. 38 CVEs found. 7 impacting your stack.
That last number is the only one that matters.
Most CVE tools flood you with every vulnerability published. This workflow reads 6 live security feeds every 6 hours - and tells you only what threatens your PostgreSQL, your Apache, your Docker, your n8n. Everything else is filtered out. No dashboard to check. No noise to wade through. Just a message that says: here's what's attacking your stack right now.
 The Problem It Solves
25,000+ new CVEs are published every year. Manual triage across BleepingComputer, CISA advisories, CVE databases, and national CERTs takes hours every day - and you still miss things. Most CVE tools give you everything and let you figure out what matters.
This workflow flips that: you define your stack once, it filters everything else out forever.
What's Included
- ✅ Complete n8n workflow JSON - import and run immediately
- ✅ Step-by-step setup guide
- ✅ Cybersecurity RSS Feed Library ( more than 20 RSS )
- ✅ Custom Stack Keywords Reference
- ✅ Fully customizable - feeds, keywords, AI models, channels, schedule
How It Works
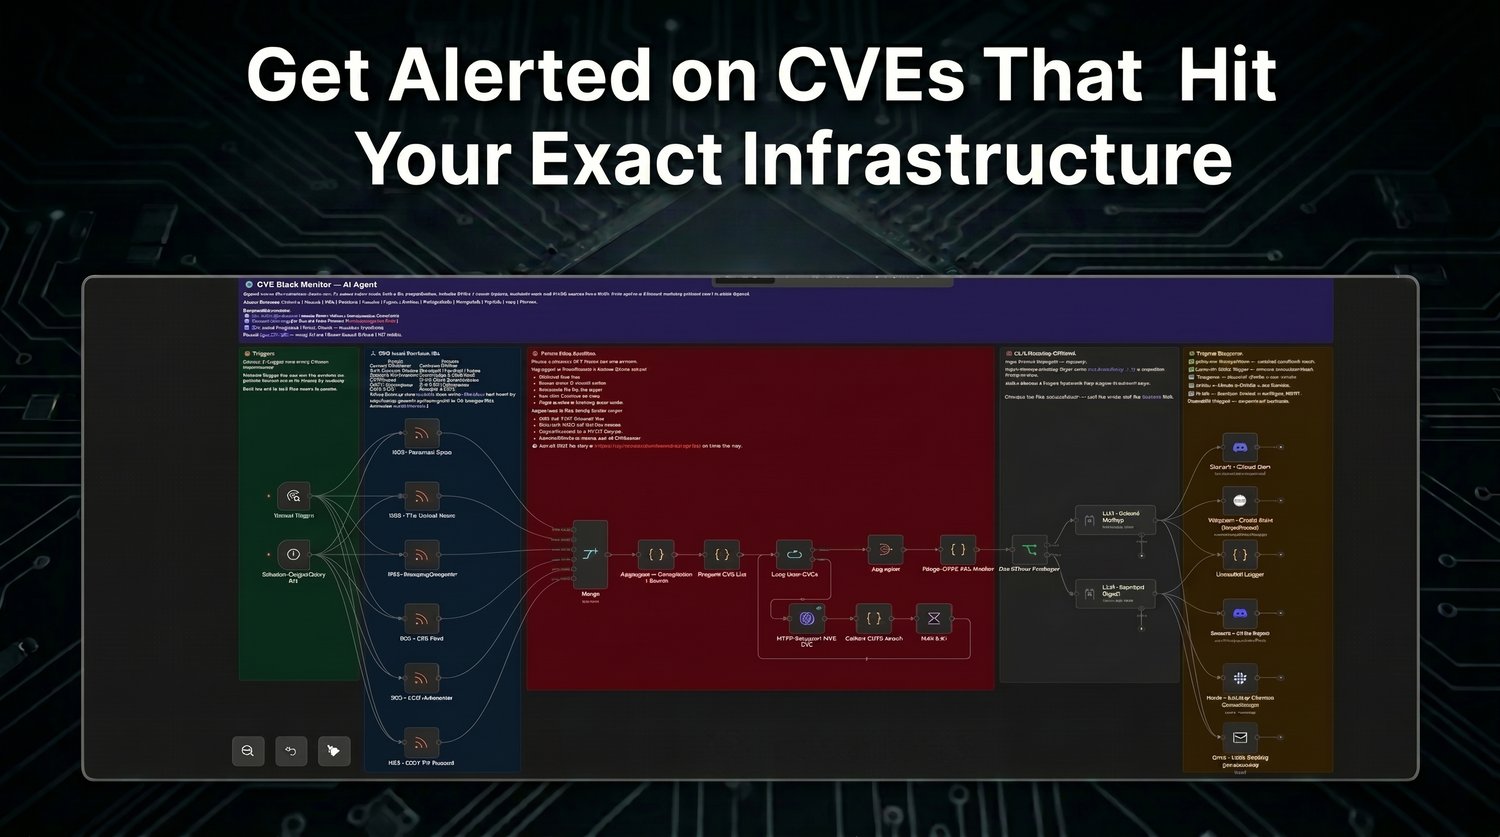
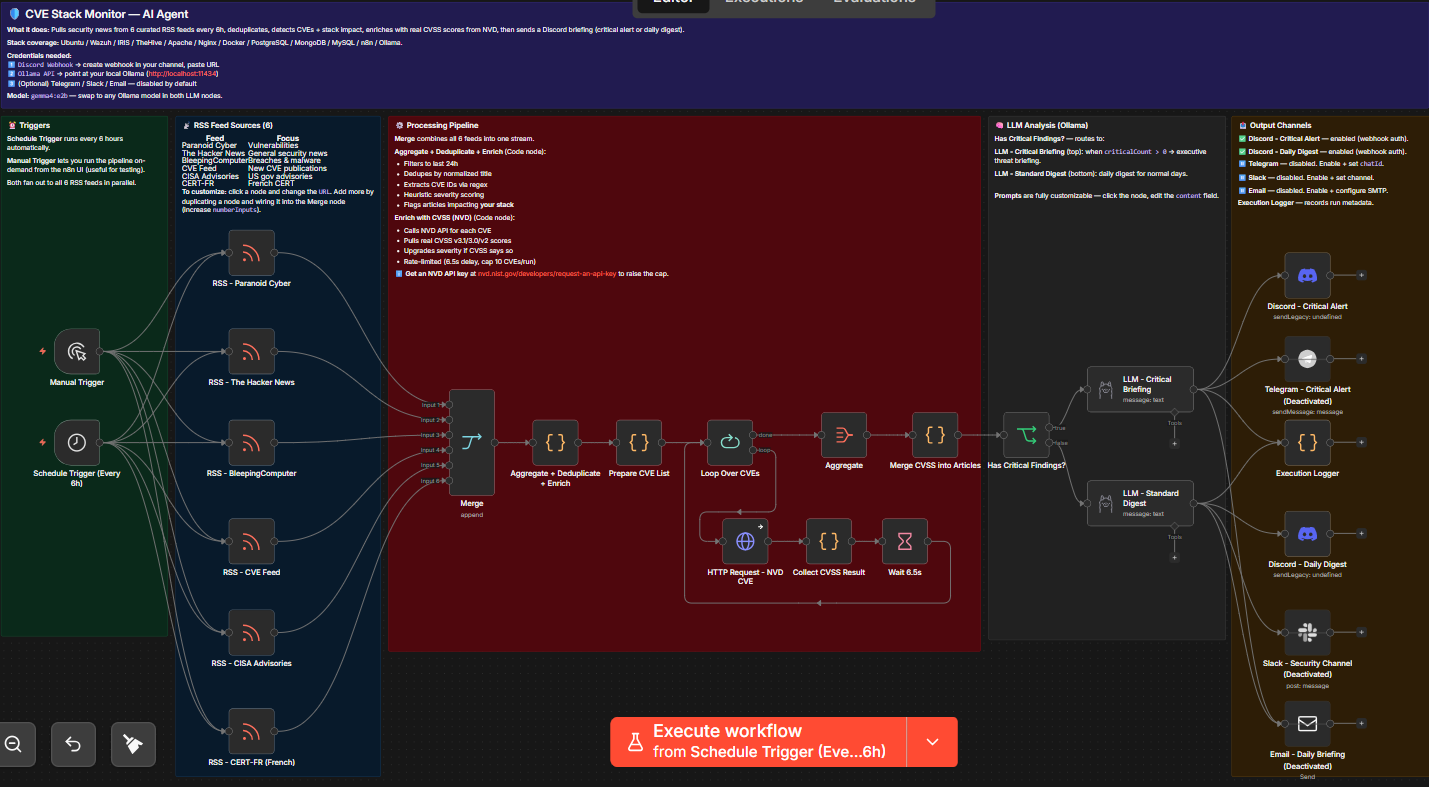
Step 1 - Ingest
Pulls from 6 curated cybersecurity feeds every 6 hours:
- Paranoid Cyber - The Hacker News - BleepingComputer
- CVE Feed (dedicated vulnerability stream) - CISA Advisories (US government) - CERT-FR (French national CERT)
All feeds merge into a single deduplicated pipeline. No duplicate articles. No noise.
Step 2 - CVE Enrichment Loop
Every CVE detected triggers a live NVD API lookup:
- Pulls real CVSS v3/v3.0 scores per CVE
- Applies heuristic severity scoring
- Flags articles that impact your defined stack keywords
- Rate-limits NVD calls responsibly (6.5s delay, capped at 10 CVEs/run)
- Extracts CVE IDs via regex for precision matching
Step 3 - AI Analysis
Connect any LLM you already use:
- Local models (Ollama, LM Studio) - no data leaves your network
- Cloud APIs (OpenAI, Anthropic, Groq, Mistral) - one field to update
- Azure OpenAI, AWS Bedrock - enterprise deployments supported
The AI generates two briefing formats:
- 🔴 Critical Briefing - fires immediately when critical CVEs hit your stack. Executive summary + ranked threats + remediation actions.
- 📊 Standard Digest - daily summary with full stats: articles scanned / CVEs found / impacting your stack.
Step 4 - Multi-Channel Alert Routing
- Discord Critical Alert - fires immediately on high-severity CVEs
- Telegram Critical Alert - parallel urgent push notification
- Discord Daily Digest - morning briefing for your SOC team
- Slack Security Channel - team-wide updates
- Email Daily Briefing - optional SMTP digest
- Execution Logger - every run logged for audit trail
Who This Is For
SOC analysts and teams tired of manually checking 6 security sources every morning.
MSPs and security consultants managing multiple clients who need automated vulnerability intelligence without paying per-client SaaS fees.
Security-conscious teams who can't send vulnerability data to cloud AI services due to compliance or data sensitivity requirements.
Built by a Practicing SOC Engineer
This workflow runs in a real multi-client SOC environment. Every node was built and tested in production - not a demo environment.
7-day guarantee
If it doesn't work as described, or it isn't what you needed, contact us within 7 days of purchase and we'll refund you in full. If you'd rather have it working, say so and we'll help you get it running. Your call. Full terms.