
CVE Explainer and PoC Fetcher - One Lookup, Not Four
You search the same CVE in four different places. Every time.
You get a CVE ID - from a scanner, a Slack alert, a vendor advisory, whatever. Then the tab-hopping starts.
NVD for the base score. CISA KEV to see if it's actively exploited. EPSS to get a sense of real-world probability. GitHub or exploit-db to check if a PoC is already public. Then you write up a summary and paste it into a ticket or an email.
That's 20–30 minutes per CVE. On a busy week, that adds up to hours of lookup work that produces no new intelligence - just aggregated data you could have automated.
This is the workflow that does it for you.
CVE Enrichment Automation n8n - What It Does
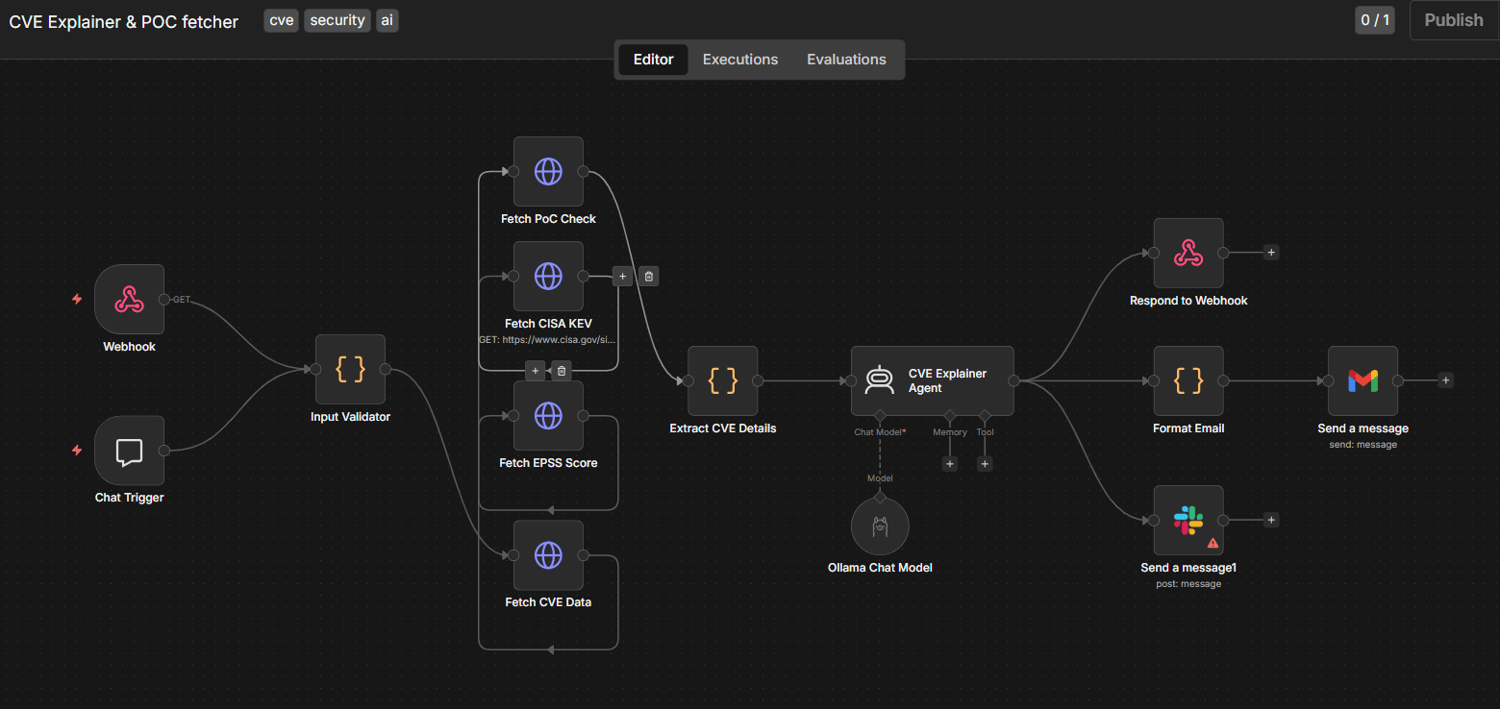
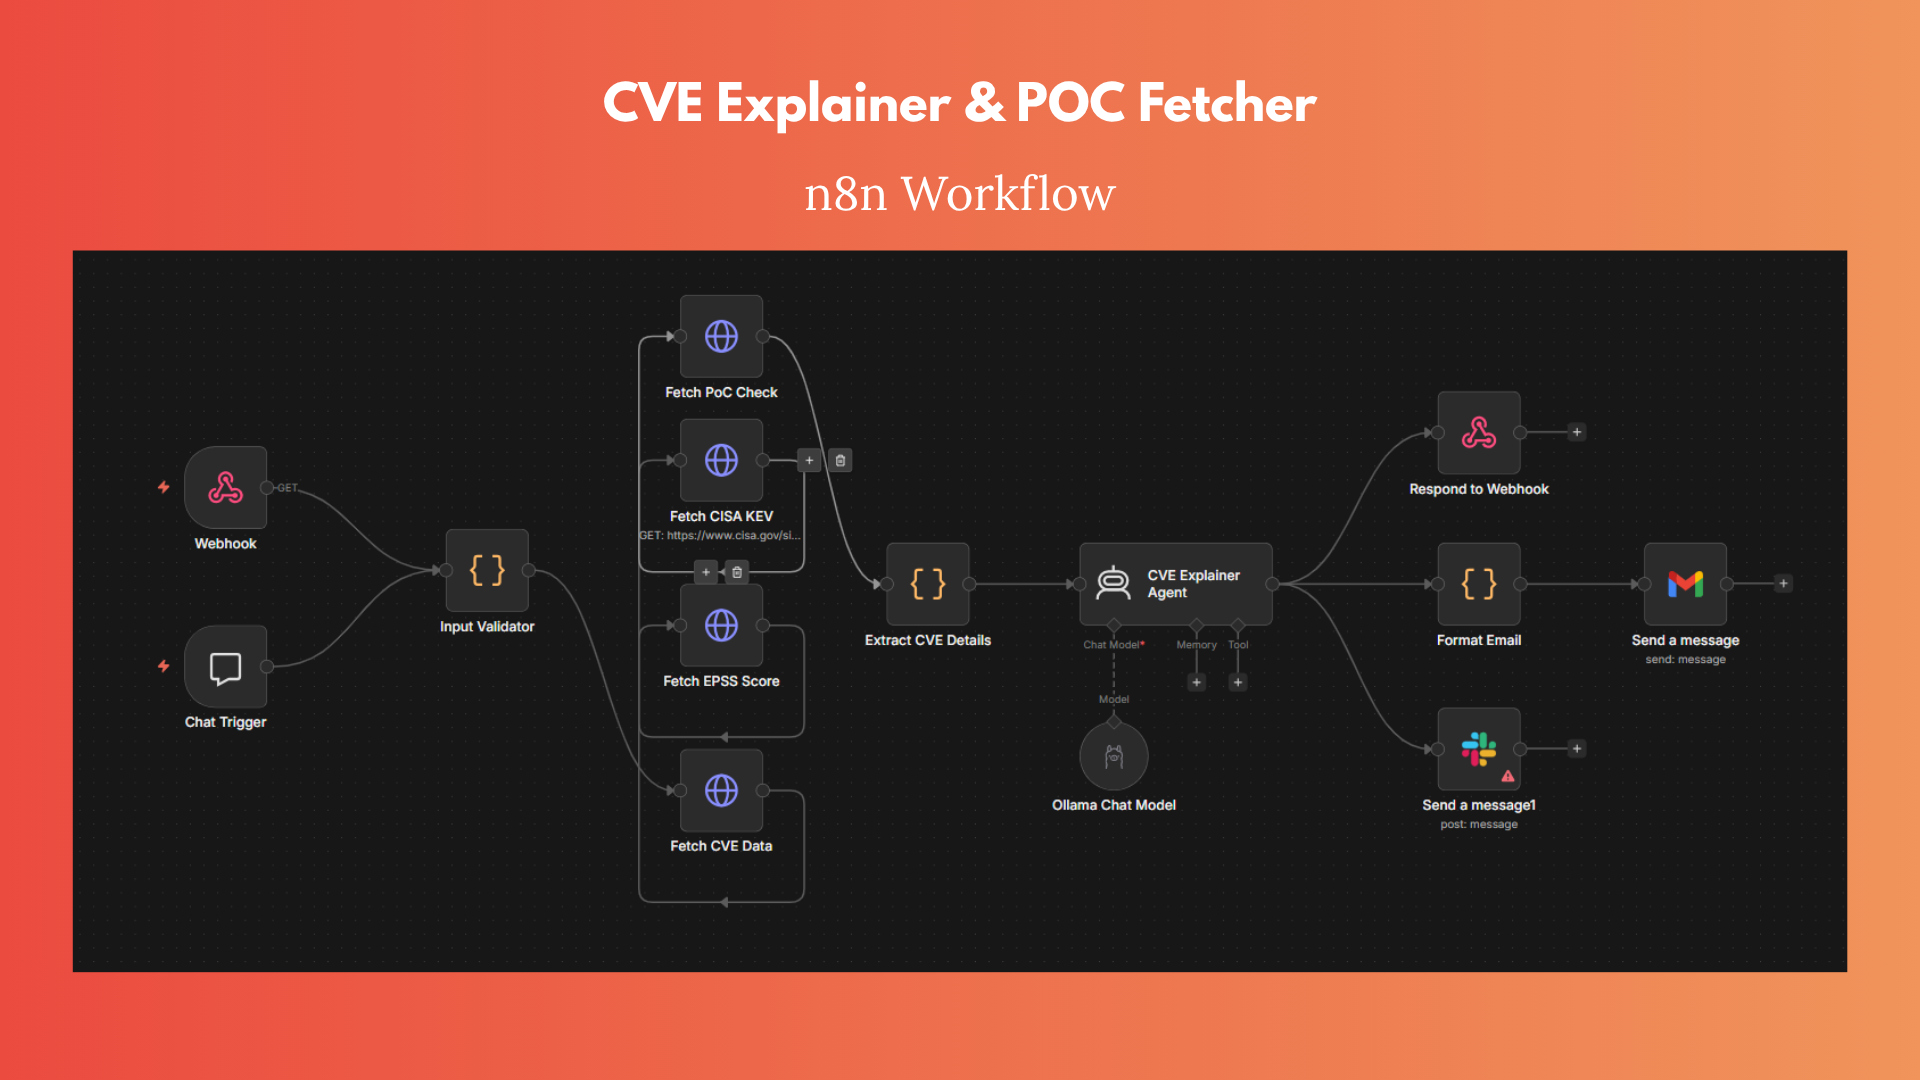 The CVE Explainer & POC Fetcher is a ready-to-import n8n workflow that takes a CVE ID - via webhook or chat - and returns a fully enriched summary in under 60 seconds. It runs four parallel data fetches, passes everything to a local AI agent, and delivers the result via email or webhook.
No subscriptions to enrichment platforms. No per-lookup fees. Your infrastructure, your data.
What's Included
- Webhook + Chat Trigger inputs - Send a CVE ID from your SIEM, a Slack command, a form, or type it directly into the n8n chat interface
- Input Validator node - Catches malformed CVE IDs before they waste API calls
- 4 parallel enrichment fetchers - Simultaneously queries PoC availability, CISA KEV status, EPSS exploit probability score, and full CVE detail data
- CVE Explainer Agent - AI Model summarizes all four data sources into a plain-language explanation with severity context and recommended action
- Email Formatter + Gmail sender - Outputs a structured email summary ready for your team's inbox or ticketing integration
- Webhook response node - Returns the enriched result as JSON for API-first integrations
- Slack output node (pre-built, deactivated) - One toggle to enable Slack notifications when you're ready
- Implementation Guide
Who This Is For
- Vulnerability management engineers who process 10+ CVEs per week and want to cut lookup time without adding tools
- SOC analysts who need quick PoC-awareness when triage decisions are time-sensitive
- MSSPs managing multiple client environments who need a repeatable, auditable enrichment pipeline
- n8n users who already have the stack and just need the workflow
Authority Signal
This workflow was built out of real operational need - the same enrichment steps that most analysts do manually, encoded into a reproducible flow. The Ollama integration means your CVE descriptions never leave your environment. The parallel fetcher design keeps total enrichment time under a minute even when two or three of the external APIs respond slowly.
7-day guarantee
If it doesn't work as described, or it isn't what you needed, contact us within 7 days of purchase and we'll refund you in full. If you'd rather have it working, say so and we'll help you get it running. Your call. Full terms.