
SIEM Use Cases + SOAR Hands-On Workshop — FREE PDF Pack
🛡️ SIEM USE CASES + SOAR HANDS-ON WORKSHOP
Detect Threats. Investigate Alerts. Understand Security Automation.
🎁 100% FREE — Download Both PDF Guides
🤝 Optional Support: If you find these resources helpful, you can optionally support the creator. No payment is required to download the free PDFs.
🚀 Learn How SIEM Detection and SOAR Automation Fit Together
Security monitoring is more than collecting logs. SOC analysts need to recognize suspicious behavior, investigate alerts, understand the evidence, and determine what action should follow.
This combined learning pack brings together two cybersecurity PDFs:
- PDF 1: SIEM Use Cases — explore real-world detection scenarios and the logic behind security alerts.
- PDF 2: SOAR Hands-On — explore security orchestration, automation, and response workflows.
Together, these resources introduce two important parts of modern Security Operations Center (SOC) work: identifying suspicious activity through SIEM detection and understanding how SOAR can help organize response workflows.
Whether you're beginning your SOC journey or strengthening your understanding of security operations, this free pack gives you a focused starting point for further study.
🔍 PDF 1 — SIEM Use Cases
Explore detection scenarios, relevant log sources, investigation logic, and example SIEM queries.
Topics include:
- Brute-Force Attacks: Understand repeated authentication failures and suspicious login patterns.
- Malware Beaconing: Explore periodic outbound connections that may indicate communication with command-and-control infrastructure.
- Impossible Travel: Understand how geographically distant login events can indicate potential account compromise.
- Privilege Escalation: Explore Windows and Active Directory events associated with suspicious account or group privilege changes.
- DNS-Based Threat Detection: Learn why DNS logs can help investigate suspicious communication and potential tunneling.
The PDF uses illustrative dashboards, event examples, and detection concepts to help explain how analysts can investigate suspicious activity.
⚙️ PDF 2 — SOAR Hands-On
Explore the concepts behind Security Orchestration, Automation and Response (SOAR).
SOAR helps security teams organize response processes by connecting tools, investigation steps, and repeatable workflows.
Use this companion PDF to explore the SOAR practical-learning material and develop a better understanding of security automation.
Important: This is an educational resource pack, not a deployed SOAR platform or a guarantee that every workflow is production-ready.
🔗 How SIEM and SOAR Work Together
A simplified security workflow looks like this:
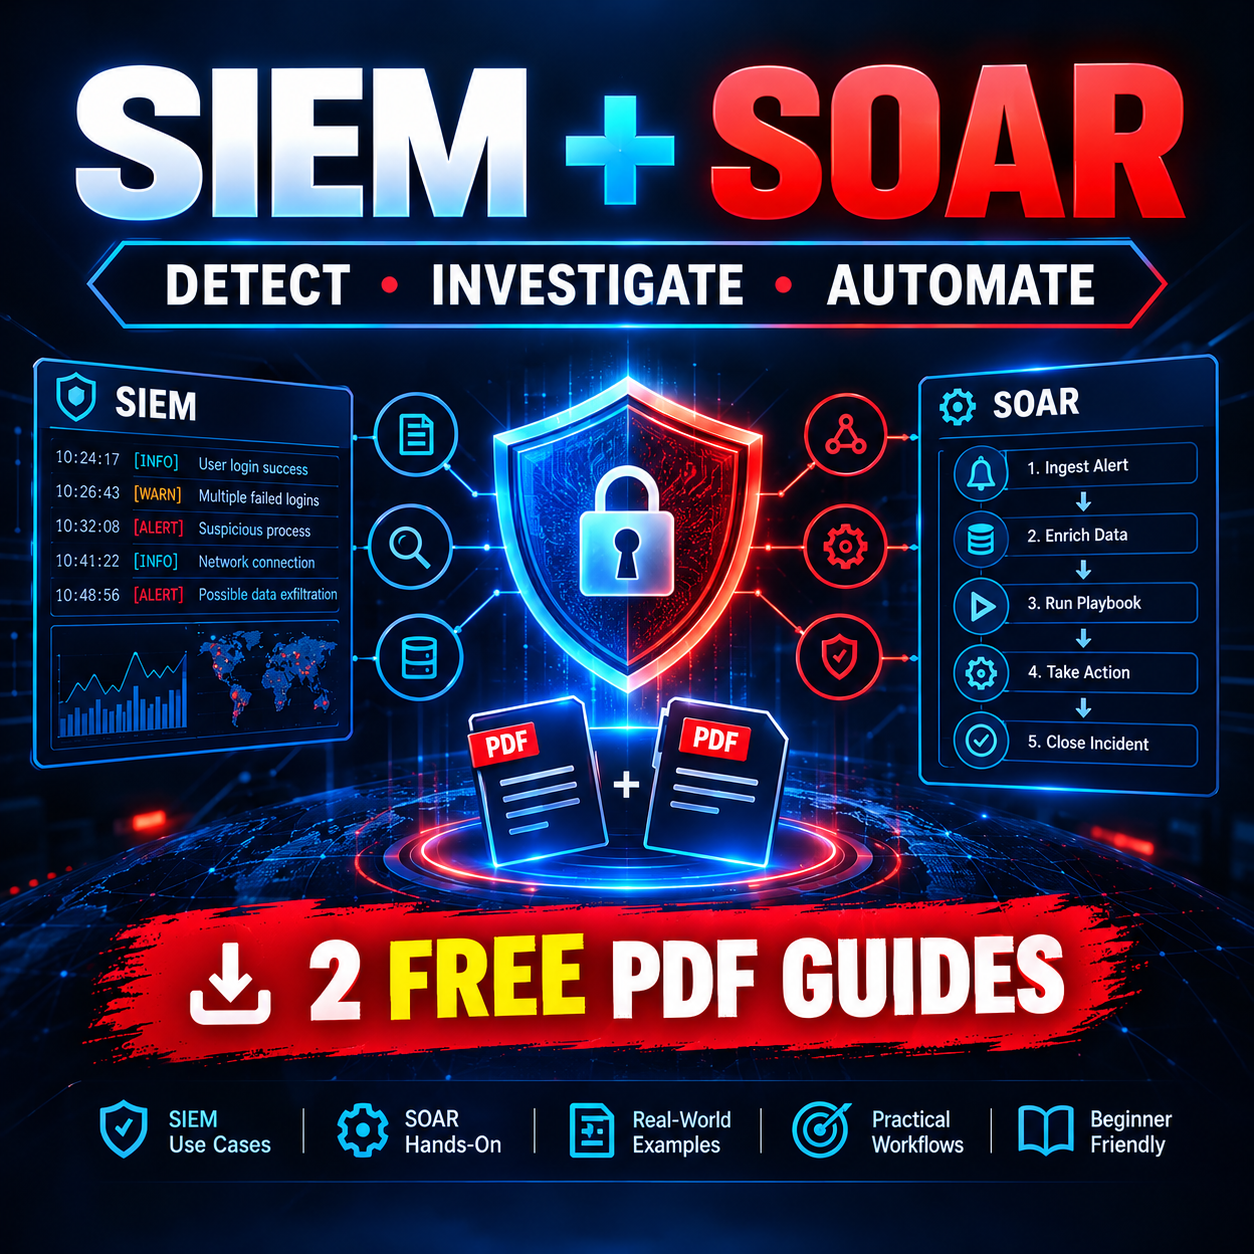
Collect Logs → Detect Suspicious Activity → Investigate the Alert → Enrich Evidence → Coordinate Response → Document Findings
- SIEM helps collect, correlate, and analyze security events.
- SOAR can help coordinate repeatable investigation and response actions.
- SOC analysts review evidence, validate findings, and make appropriate decisions.
Learning how these functions complement one another can help you understand the broader SOC ecosystem.
📦 What's Included
Your free download includes two PDF files:
- Demo SIEM Use Cases by Amresh — 13 pages.
- Demo SOAR Hands-On by Amresh — 10 pages.
Total: 23 pages across two PDFs.
No separate paid course or software subscription is required to receive these files.
🎯 Who Is This For?
This learning pack is suitable for:
- Aspiring SOC analysts
- Cybersecurity beginners
- IT and computer science students
- Junior security analysts
- SIEM learners
- Security monitoring enthusiasts
- Learners exploring detection engineering
- Cybersecurity students interested in SOAR and automation
- Anyone building foundational knowledge of security operations
🚫 Who Shouldn't Get This?
This may not be the right resource if you're looking for:
- A complete advanced SOC certification course
- A fully configured SIEM or SOAR lab
- Production-ready automation playbooks guaranteed to work in your environment
- Detailed installation instructions for every security platform
- A guarantee of employment or certification success
These PDFs are introductory learning resources. Hands-on practice, official documentation, and further study are needed to build operational skills.
📚 Want the Complete SOC Level-2 Notes?
Looking for a more extensive learning resource covering SOC Level-2 responsibilities, alert investigation, log correlation, detection engineering, threat hunting, incident response, Python for SOC, SOAR automation, portfolio projects, and interview preparation?
Explore the separate SOC Analyst L2 Complete Guide here:
Please note: This is a separate Payhip product and may require payment. It is not included in the two free PDFs offered on this page.
⚠️ Important Notes
- The included PDFs are educational resources.
- Tool interfaces, event IDs, queries, and integrations can vary by environment and software version.
- Validate detection logic and response steps before using them operationally.
- Investigate only systems and accounts you are authorized to assess.
- Follow your organization's incident response procedures and evidence-handling requirements.
❓ Frequently Asked Questions
Is this product free?
Yes. Both PDFs are offered free of charge.
What will I receive?
Two PDFs: a 13-page SIEM Use Cases guide and a 10-page SOAR Hands-On guide.
Do I need a paid subscription?
No paid subscription is required to download these PDFs. Individual tools mentioned or used in further practice may have their own requirements.
Is this suitable for beginners?
Yes. The pack is intended as an introduction to SIEM detection scenarios and SOAR concepts. Some security terminology may require additional research.
Does it include a complete working SIEM or SOAR lab?
No. The product contains PDF learning resources, not a ready-to-run lab environment.
Where can I find the complete SOC L2 notes?
Visit the separate resource: https://payhip.com/b/VRlpu. Check its current price and included materials on Payhip.
Is optional support required?
No. Support is voluntary, and the two PDFs are free.
🎁 Get Both PDFs for FREE
Start exploring security detection and automation with two focused learning resources.
🛡️ SIEM Use Cases + SOAR Hands-On
Learn the detection concepts. Understand the response workflow. Continue building your cybersecurity knowledge.
Download both PDFs for free and take your next step into SOC learning.