
Threat Intel Analyst: AI Threat Intelligence
On Sale
$67.99
$67.99
Read a threat report. Know in seconds if you are affected
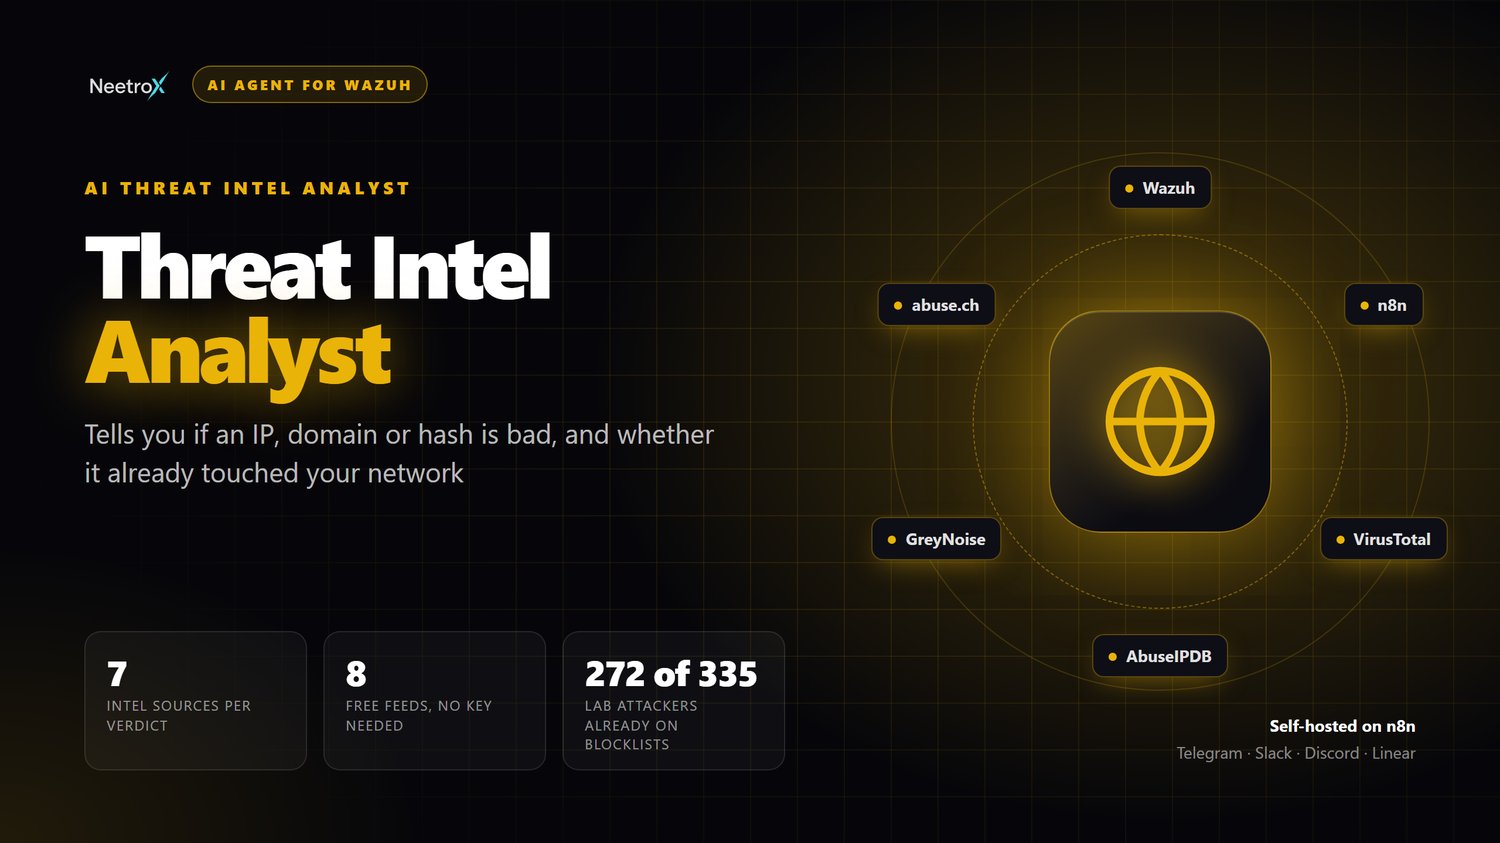
It checks every indicator against 7 intel sources and your own Wazuh logs, so each answer says whether it is bad, whether it touched your hosts and what to do next.
Knowing an IP is bad is useless until you know it hit you
Today: ten tabs and a guess
- Paid feeds, or ten free sites checked one by one
- Threat reports read, never checked against your logs
- Known attackers let through the firewall
With the Threat Intel Analyst: an answer with evidence
- One verdict from 7 sources, with the reasons
- Every indicator matched to your hosts, with when and which direction
- Perimeter block lists from the attackers already hitting you
Enterprise threat intel without enterprise feeds
- IOC verdicts: VirusTotal, AbuseIPDB, OTX, GreyNoise and abuse.ch ThreatFox, URLhaus and MalwareBazaar, with reasons and where it appears in your alerts
- Report to hunt: Paste a report or a link. It pulls out IPs, domains, URLs, hashes, CVEs and ATT&CK ids, refangs them and checks your logs
- Daily feed sweep: 8 free feeds, including Feodo C2, Spamhaus DROP, Emerging Threats and Tor exits, matched against Wazuh with severity by context
- Hit journal: See what is new, what got worse and what came back after you closed it
- Watchlist: Your own indicators with verdict, confidence, TLP, actors and expiry, plus an allowlist, retro-hunted over up to a year of alerts
- Real-time enforcement: The watchlist pushed into Wazuh as CDB lists and rules, with your approval, a logtest canary and automatic restore
- Landscape brief: New CISA KEV entries checked against your hosts, live botnet C2 servers and malware trends
- Share: STIX 2.1 with TLP markings, plain blocklists, CSV and Wazuh CDB. TLP:RED never leaves unless you say so
- HTML report: KPIs, important hits, watchlist activity and the narrative, delivered in your chat
One command, about ten minutes
- Install: Run one command on Linux, macOS or Windows. It deploys n8n too if you need it
- Connect: Add a Wazuh indexer user, your chat app and an AI model key. Each free intel key adds a source
- Ask: Paste an indicator or a report. The daily sweep starts on its own
Fast verdicts, careful actions
- One action, approved: Pushing the watchlist into Wazuh needs an Approve click, starts in dry run and backs up every file
- Restored on failure: Each push is checked with a logtest canary and config validation. If a check fails, every file is restored
- Private stays private: Private IPs are never sent out, and internal URLs are never fetched
- Facts from the sources: Verdicts and counts come from the sources and your logs. A missing source is reported, never guessed
- Reports are data: Report text, web pages and feed contents are never treated as instructions
- TLP respected: TLP:RED never leaves in an export unless you say so
What you need
- n8n: n8n 2.34 or newer with Agents and Data Tables, with outbound HTTPS to the feeds
- Wazuh: Wazuh 4.x with an indexer user for wazuh-alerts-*. Vulnerability states are optional, for the KEV check
- Chat app: Telegram, Slack, Discord or Linear. A Telegram bot takes a minute with @BotFather
- AI model: An API key from any provider in the n8n Agent model picker
- Intel keys: Optional and free: VirusTotal, AbuseIPDB, OTX and abuse.ch. It works without them on the free feeds
What you get
- 10 tool workflows and the daily sweep
- The agent with 6 skills: IOC triage, report to hunt, daily sweep, watchlist, hit triage and intel sharing
- One-command installer for Linux, macOS and Windows
- Setup guide and example conversations
- Single-organization commercial license
- 7-day money-back guarantee
Full details and a demo: neetrox.com/ai-agents/threat-intel-analyst