
Zero-Trust Security Explained Simply: A Practical Guide for 2026
On Sale
$12.00
$12.00
You’ve heard “zero-trust” everywhere, but nobody explains what to actually do about it. This guide does.
Zero-Trust Security Explained Simply is an 18-page, plain-English guide that turns one of cybersecurity’s biggest buzzwords into steps you can take this week. Every term is defined the first time it appears, and every section ends in something you can act on.
What’s inside
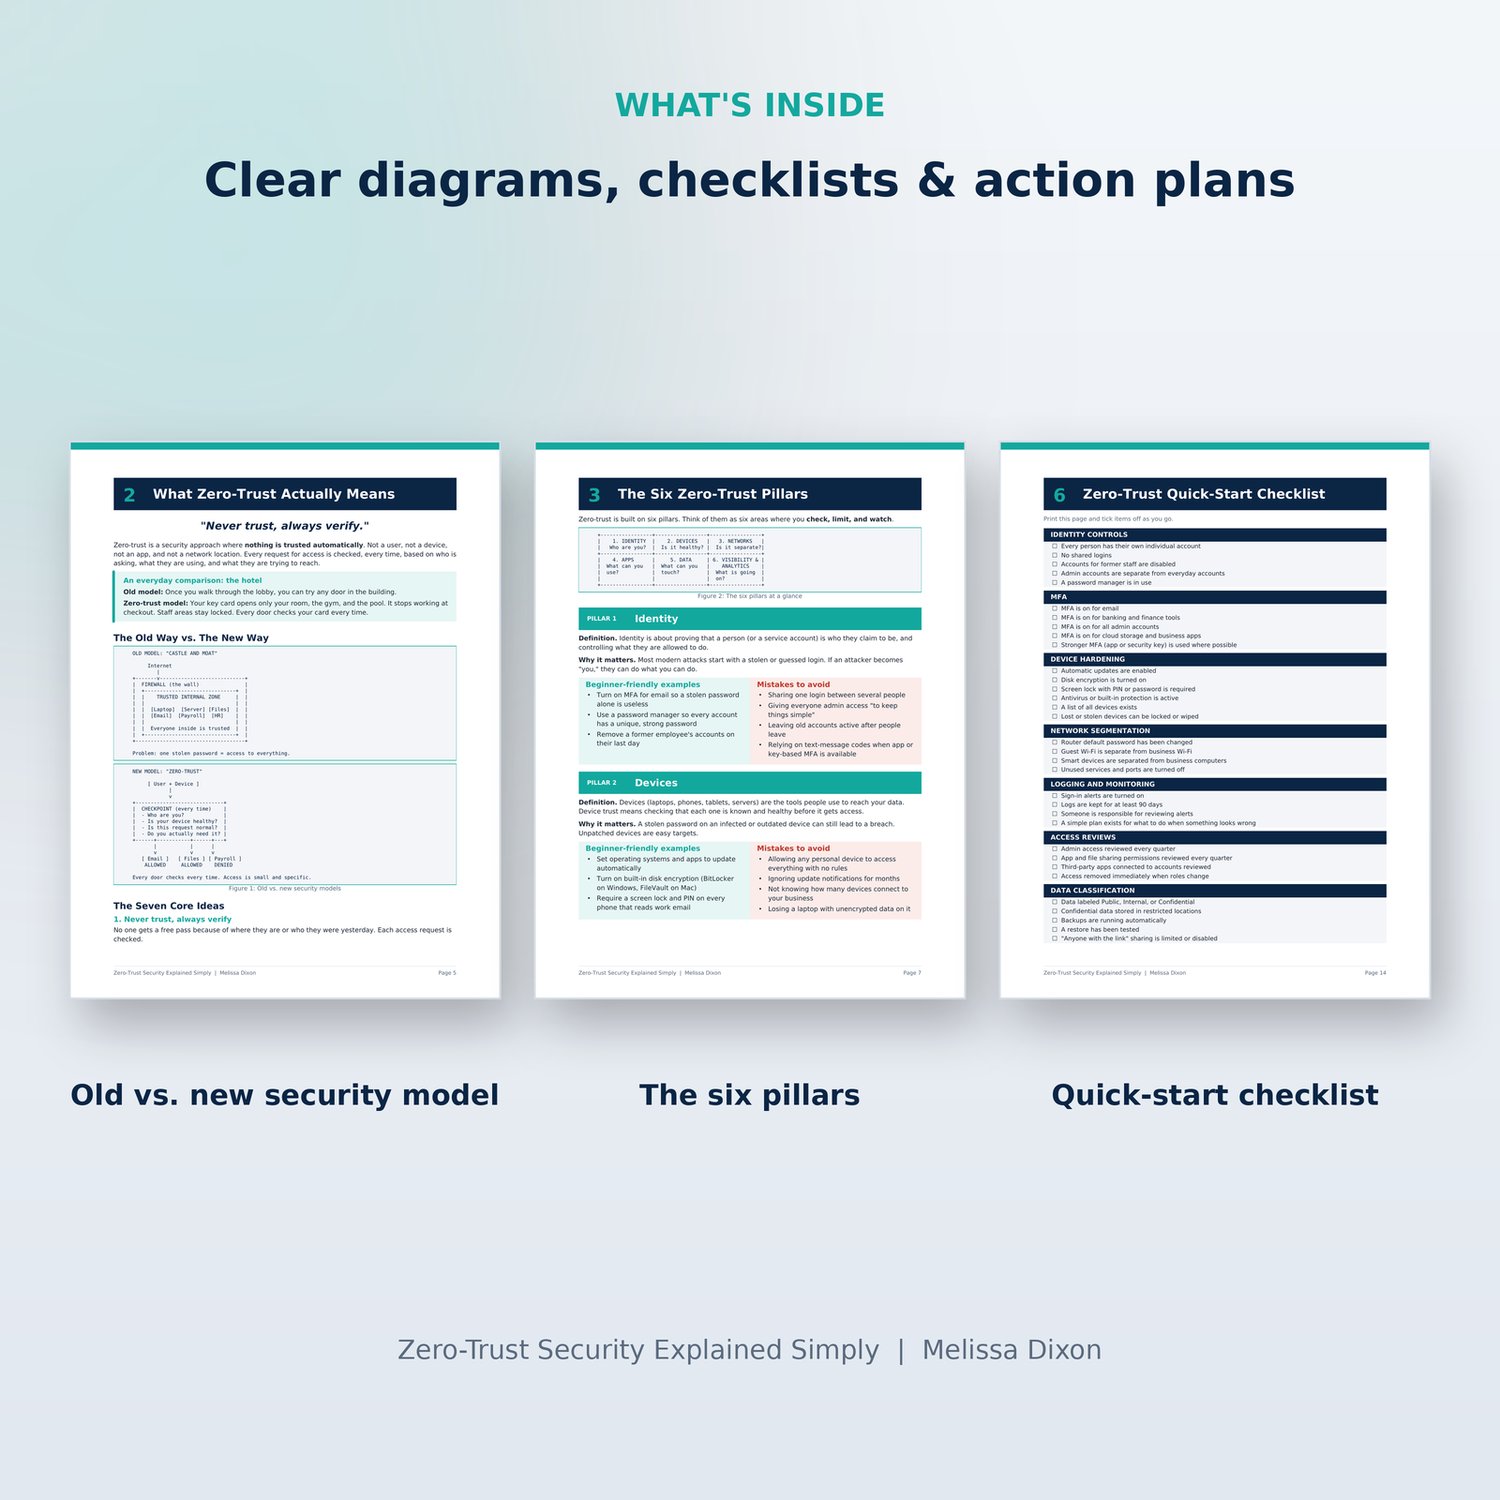
- Why the old “castle and moat” security model is failing, and what changed by 2026
- The seven core zero-trust ideas, explained with everyday comparisons and simple diagrams
- The six pillars (identity, devices, networks, applications, data, visibility), each with examples and common mistakes to avoid
- A small-business playbook with free and low-cost tools and a week-by-week 30-day roadmap
- Six hands-on exercises and lab habits for beginners
- A printable Quick-Start Checklist covering MFA, device hardening, segmentation, logging, access reviews, and data classification
- A 10-step “In 1 Hour” Crash Plan for immediate improvement
- A myths-and-mistakes page that shows you how to spot vendor marketing traps
Who it’s for
- Small business owners who want to protect their company without hiring a security team
- New cybersecurity learners and IT beginners building their foundations
- Anyone who has heard “zero-trust” and wants to finally understand it
What you’ll be able to do
- Explain zero-trust to anyone in plain language
- Lock down logins, devices, and file sharing with tools you may already have
- Use the checklist and roadmap to keep improving a little each month
File details
- Format: PDF
- Length: 18 pages
- Instant download; print-friendly checklists
- Personal and internal business use license (see the license page inside)
Written by Melissa Dixon, cybersecurity engineer and threat analyst.