
Information Security Incident & Breach Response Kit (Excel + Word) — the register, the POPIA s22 decision, the Regulator pack, the notices and two tabletop exercises
The incident process is where an ISMS is tested in public — and in South Africa it is tested against a law with no materiality threshold and a Regulator that now accepts notifications only through its portal. Most organisations find out what their procedure is missing on the day. This kit is built so you find out at a tabletop instead.
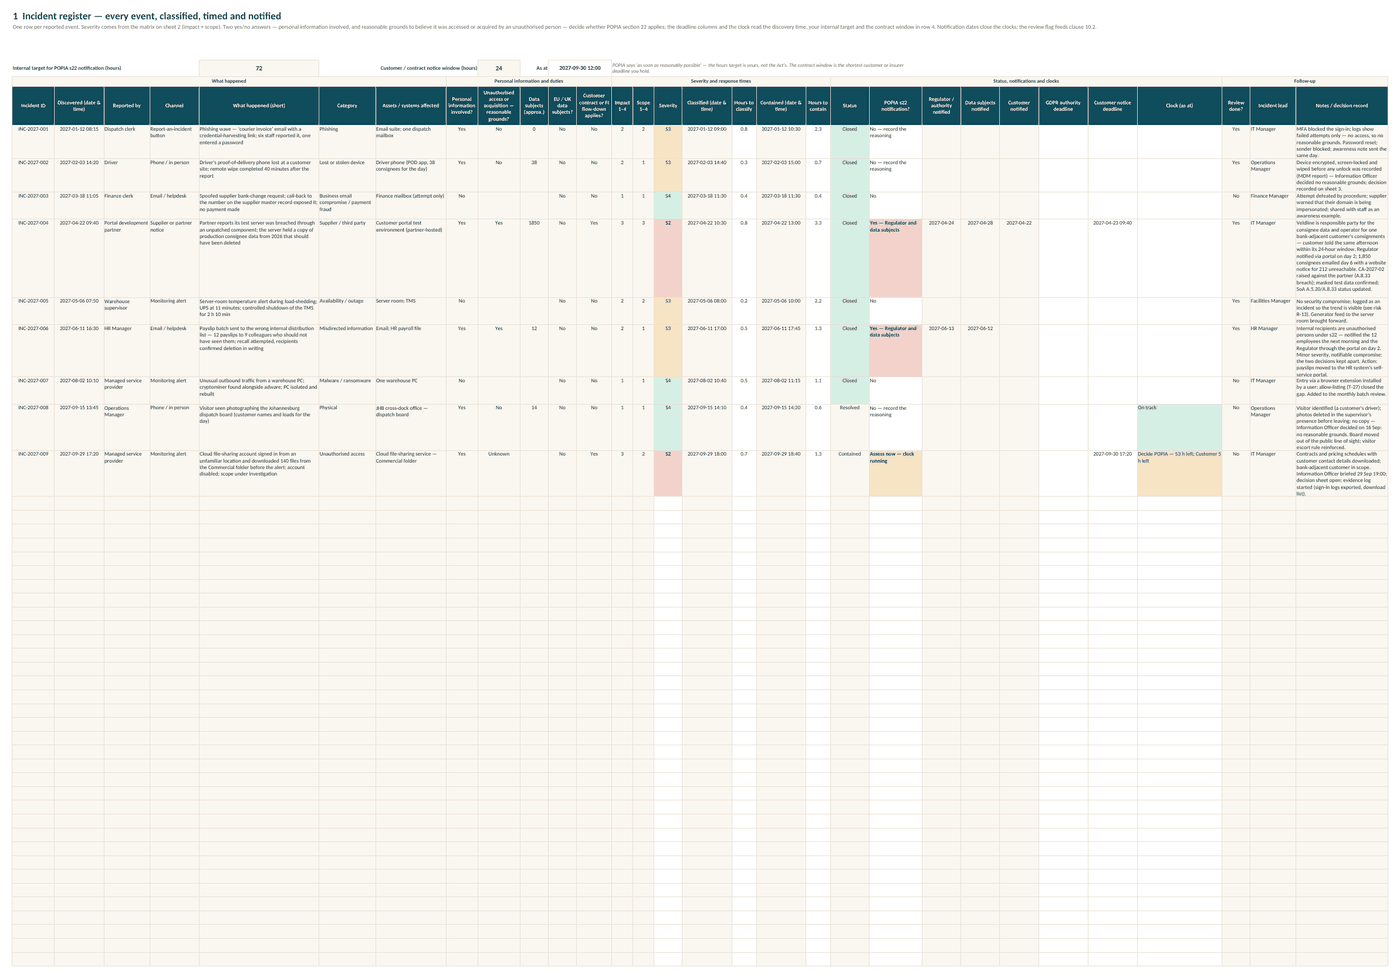
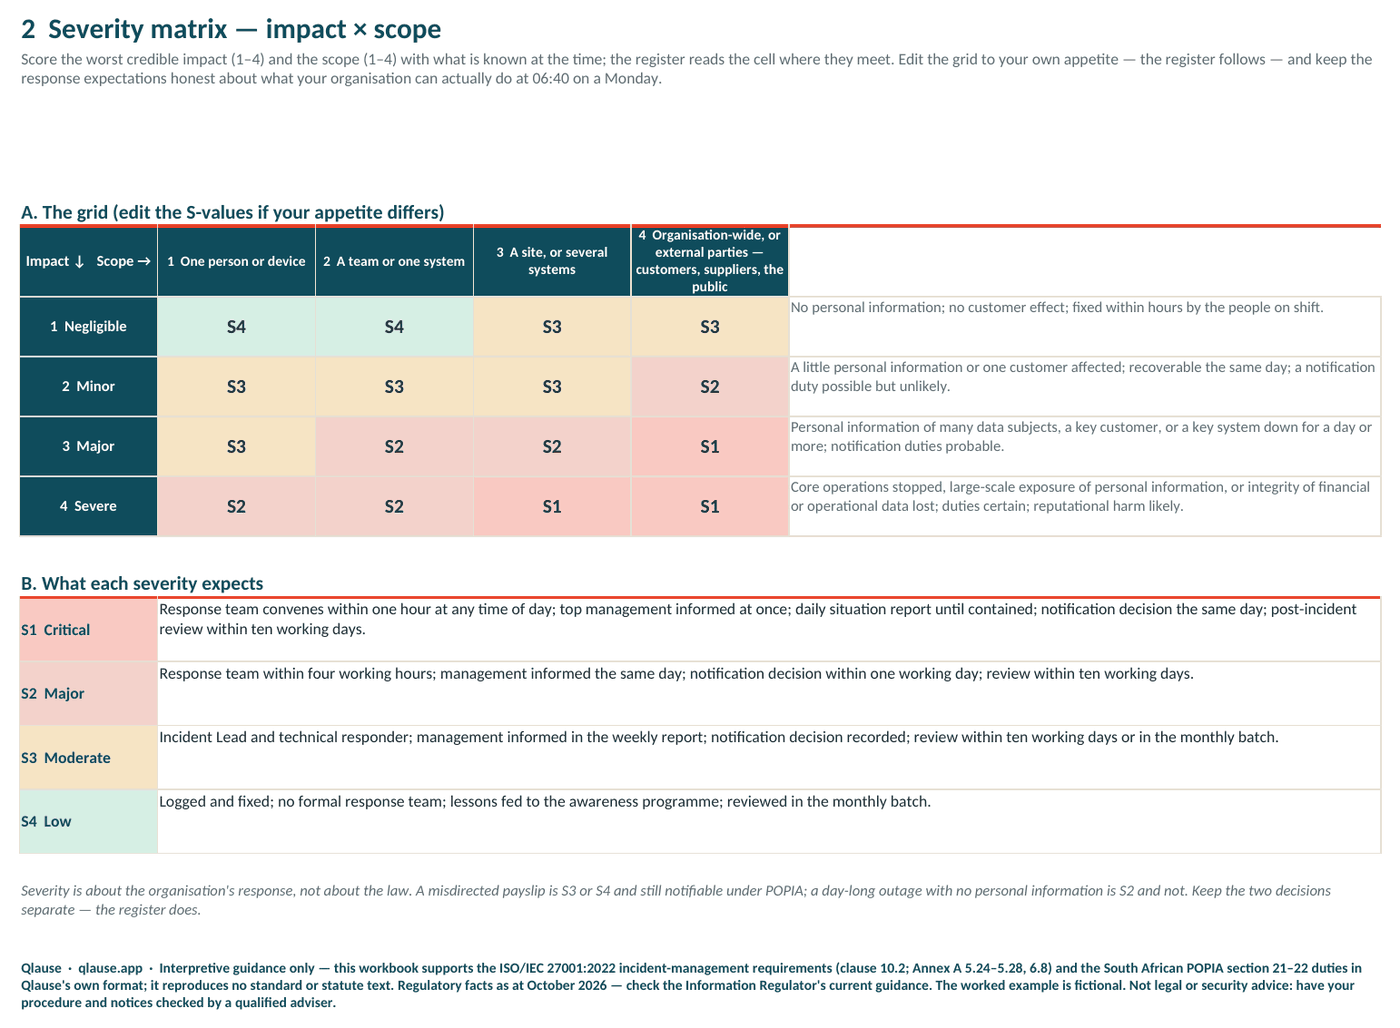
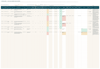
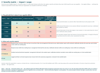
A register that keeps the clocks. One row per event. Two yes/no answers — personal information involved; reasonable grounds that it was accessed or acquired by an unauthorised person — decide whether POPIA section 22 applies, and the register says so in words. Severity comes from an editable impact × scope matrix. Discovery, classification and containment times give hours-to-classify and hours-to-contain. Your own notification target (the Act says "as soon as reasonably possible" and sets no hours — 72 is a defensible promise), the GDPR's 72 hours where EU or UK people are involved, and the shortest customer or insurer window you hold all run in a live clock column that counts down and turns coral when a deadline passes.
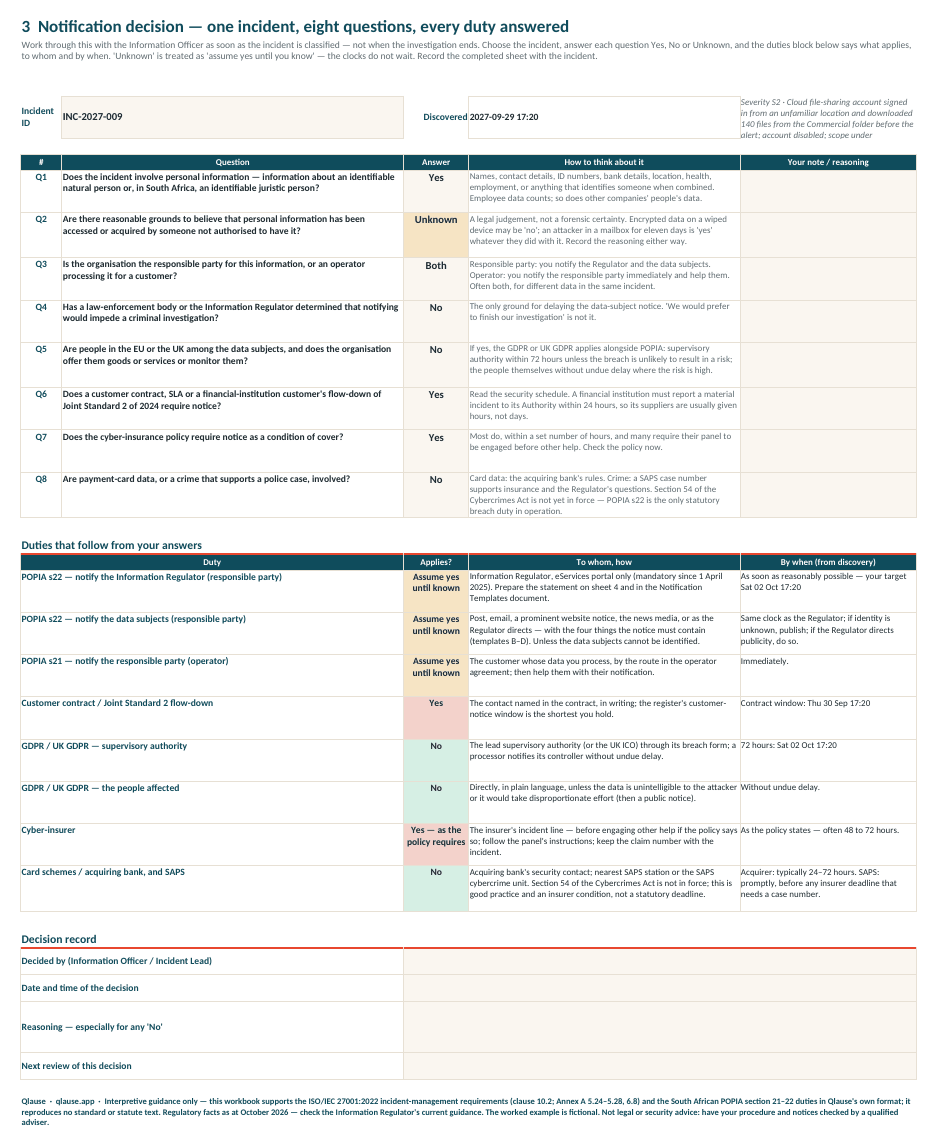
A notification decision you can defend. Eight questions for one incident — personal information, reasonable grounds, responsible party or operator, law-enforcement delay, EU/UK data subjects, customer and Joint Standard 2 flow-down, cyber-insurance, card data and police — and a duties block that answers each: applies or not, to whom, by when, with the deadline calculated from the discovery time. "Unknown" is treated as "assume yes until you know", because the clocks do not wait.
The pack for the Information Regulator's eServices portal (mandatory since 1 April 2025): thirteen things to have ready with where each comes from, the data-subject method choice under section 22(4), and a timeline from discovery to acknowledgement. Plus a Word document of notification templates — the structured statement for the portal, an email, a letter and a website notice to data subjects, each carrying the four things section 22(5) requires in plain language, and a record of notices sent.
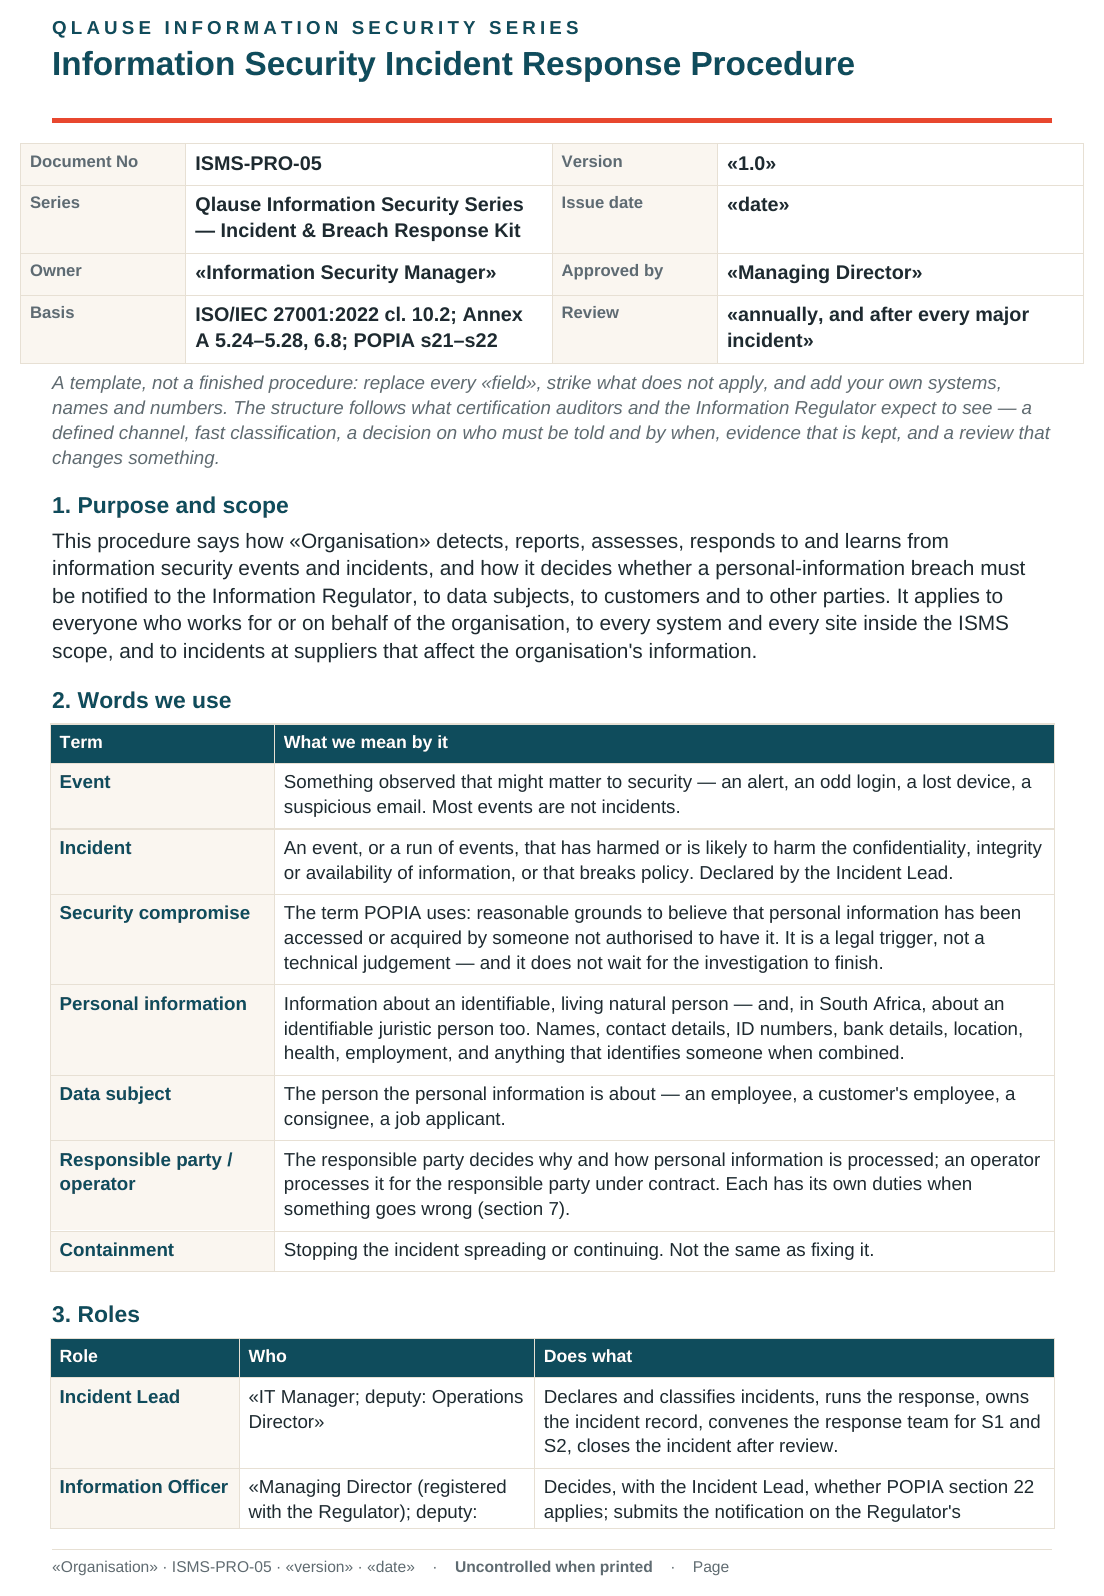
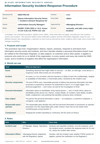
ISMS-PRO-05, the procedure (Word, five pages): roles, the reporting channel, triage and the severity matrix, containment-eradication-recovery, who must be told and by when (POPIA s21 and s22, contracts and Joint Standard 2, GDPR, insurer, card schemes, SAPS — with the Cybercrimes Act s54 position stated correctly), evidence, review, records, testing, and a contact card to print and keep off the network.
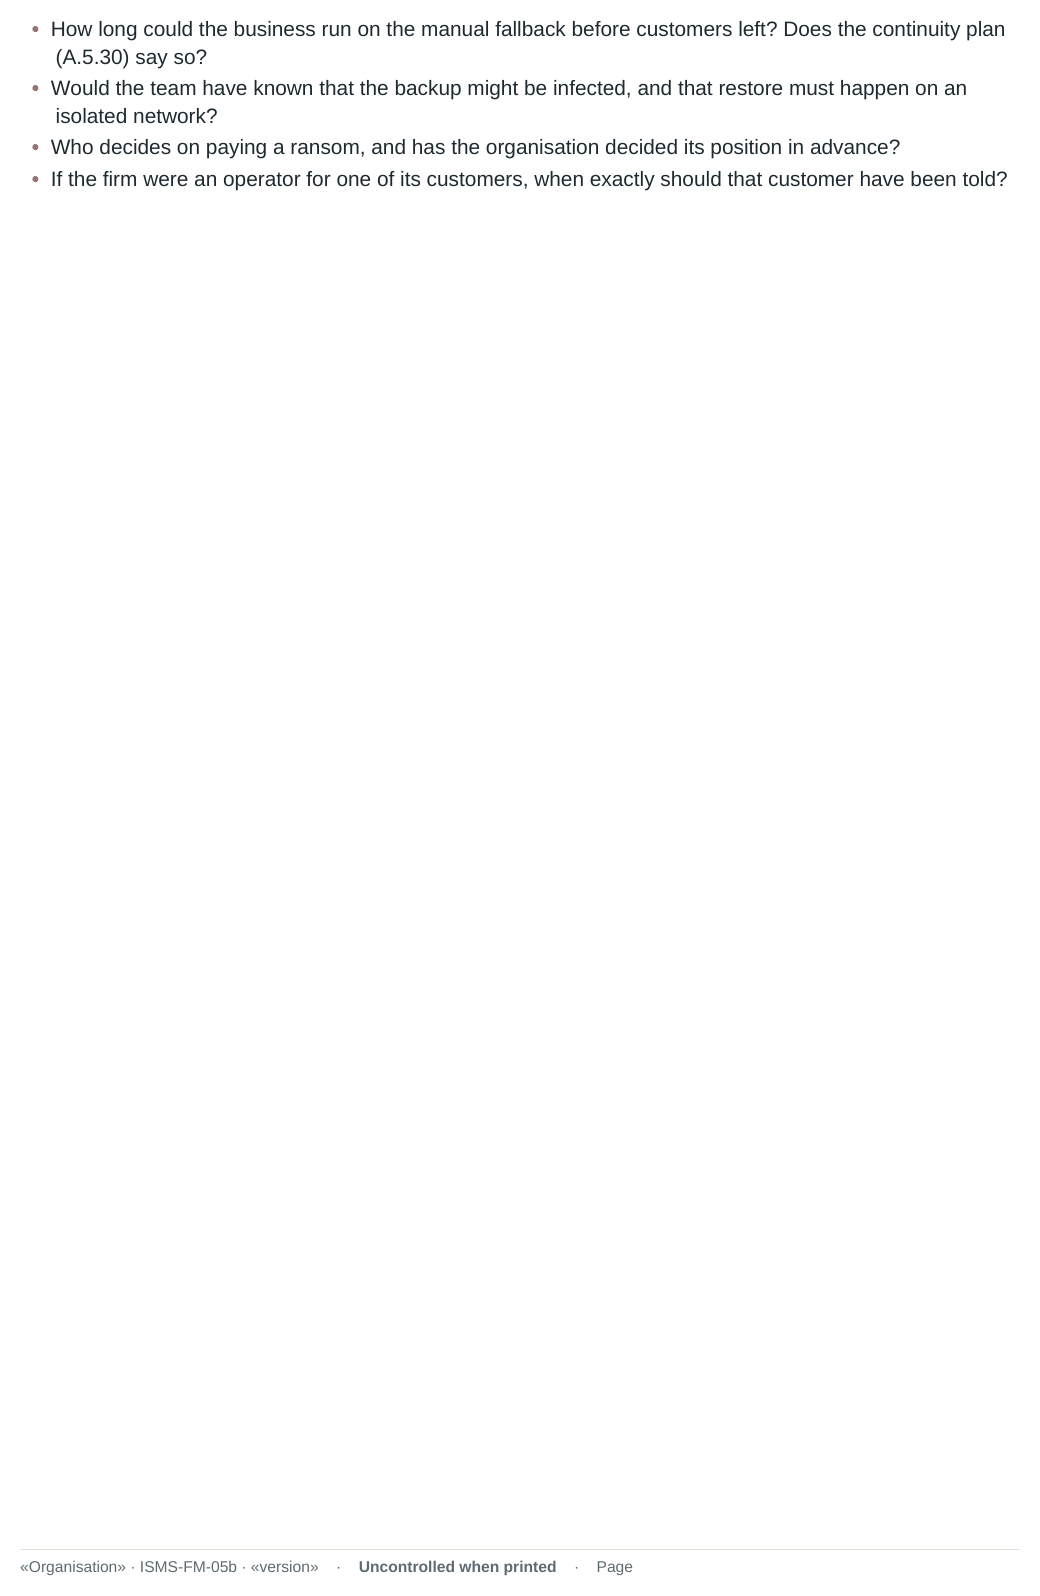
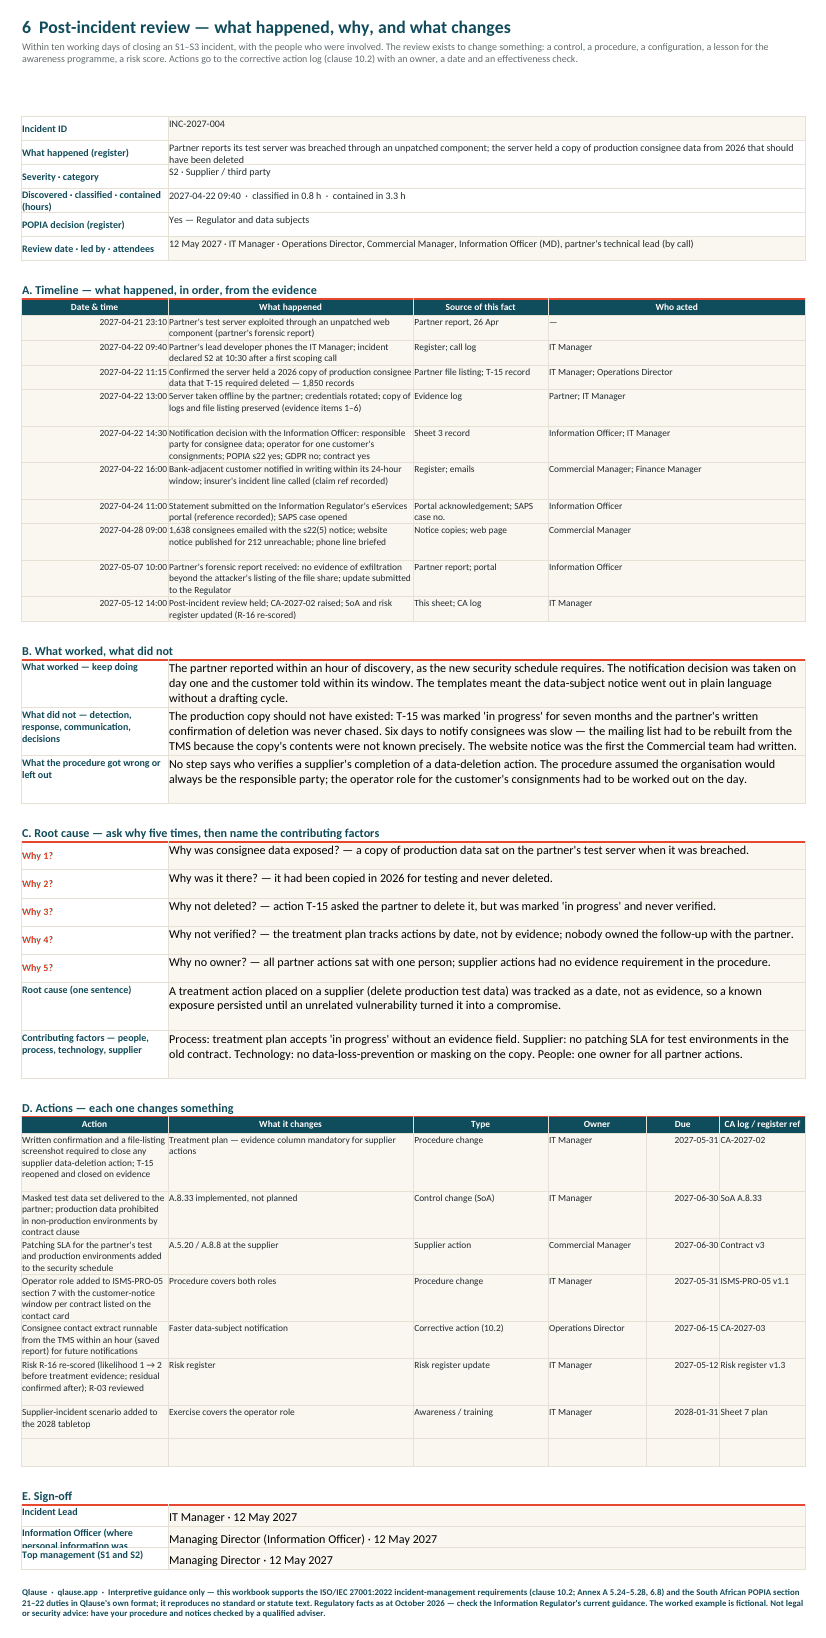
An evidence log (chain of custody), a post-incident review that walks timeline → what worked → five whys → root cause → actions that each change something and feed clause 10.2, and a tabletop record with a ten-point observer checklist, scored.
Two tabletop exercise scripts (Word): ransomware on the operational server, and a business email compromise with a diverted payment — 90 minutes each, six timed injects, the questions to ask, what a good response includes, discussion questions and a debrief record.
A worked example on the same fictional firm as the other Qlause ISO 27001 tools: nine incidents in Veldline Logistics' 2027 — a phishing wave stopped by MFA, a lost driver's phone, a spoofed bank-change caught by call-back, a supplier's test server holding production data, misdirected payslips, a cryptominer, a visitor photographing a dispatch board, and a cloud account accessed from an unfamiliar location that is still open — with the POPIA answer and the clocks live on each, and the full review of the supplier incident.
Built by working management-system auditors for a 50-to-500-person organisation without a security operations centre. No macros, no add-ins.
What's inside
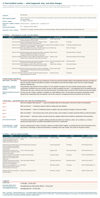
- Workbook (eleven sheets): Start here · Incident register · Severity matrix · Notification decision · Regulator checklist · Evidence log · Post-incident review · Tabletop record · Guidance · Example register · Example review.
- ISMS-PRO-05 Incident Response Procedure (template) — Word + PDF.
- Notification Templates — Information Regulator and Data Subjects (POPIA s22) — Word + PDF.
- Tabletop Exercise Scripts — Ransomware and Business Email Compromise — Word + PDF.
Who it's for
Information Officers, ISMS leads, IT managers and quality or compliance managers in South African organisations running or building an ISO/IEC 27001 system — and anyone who has been told "you are the Information Officer now" and wants to know what to do on the day.
Why buy it
- See exactly what's inside before you buy — the sheets and documents are previewed above.
- Instant download, secure checkout (Visa, Mastercard, PayPal).
- Single-organisation licence — use it across your whole organisation, no per-user fees.
- Plain Excel and Word (2016 or later, or LibreOffice) — nothing to install, no macros.
Pairs with: the Risk Assessment & SoA Toolkit and the Metrics & Evidence Tracker. Start free: the ISO 27001:2022 Gap Analysis Checklist, every clause and control explained in the Clause Explorer, and the free ISO 27001 masterclass.
Independent template in Qlause's own words. It supports the ISO/IEC 27001:2022 incident-management requirements (clause 10.2; Annex A 5.24–5.28, 6.8) and the South African POPIA section 21–22 duties without reproducing any standard or statute text; read the Act, the Information Regulator's current guidance and your licensed copy of the standard. Regulatory facts as at October 2026. The worked example is fictional. Not legal or security advice — have your procedure and notification wording checked by a qualified adviser. Qlause is an independent templates and training provider, not a certification body and not a law firm.