
AI Security for Defenders and Attackers (2026 Edition)
AI is being wired into inboxes, help desks, document stores and payment flows faster than companies can hire people who understand the risks. This book teaches you to be one of those people.
It goes past the prompt-injection hype. You get a clear mental model of how AI systems actually work, why they can be manipulated in ways normal software can’t, and what defenders do about it.
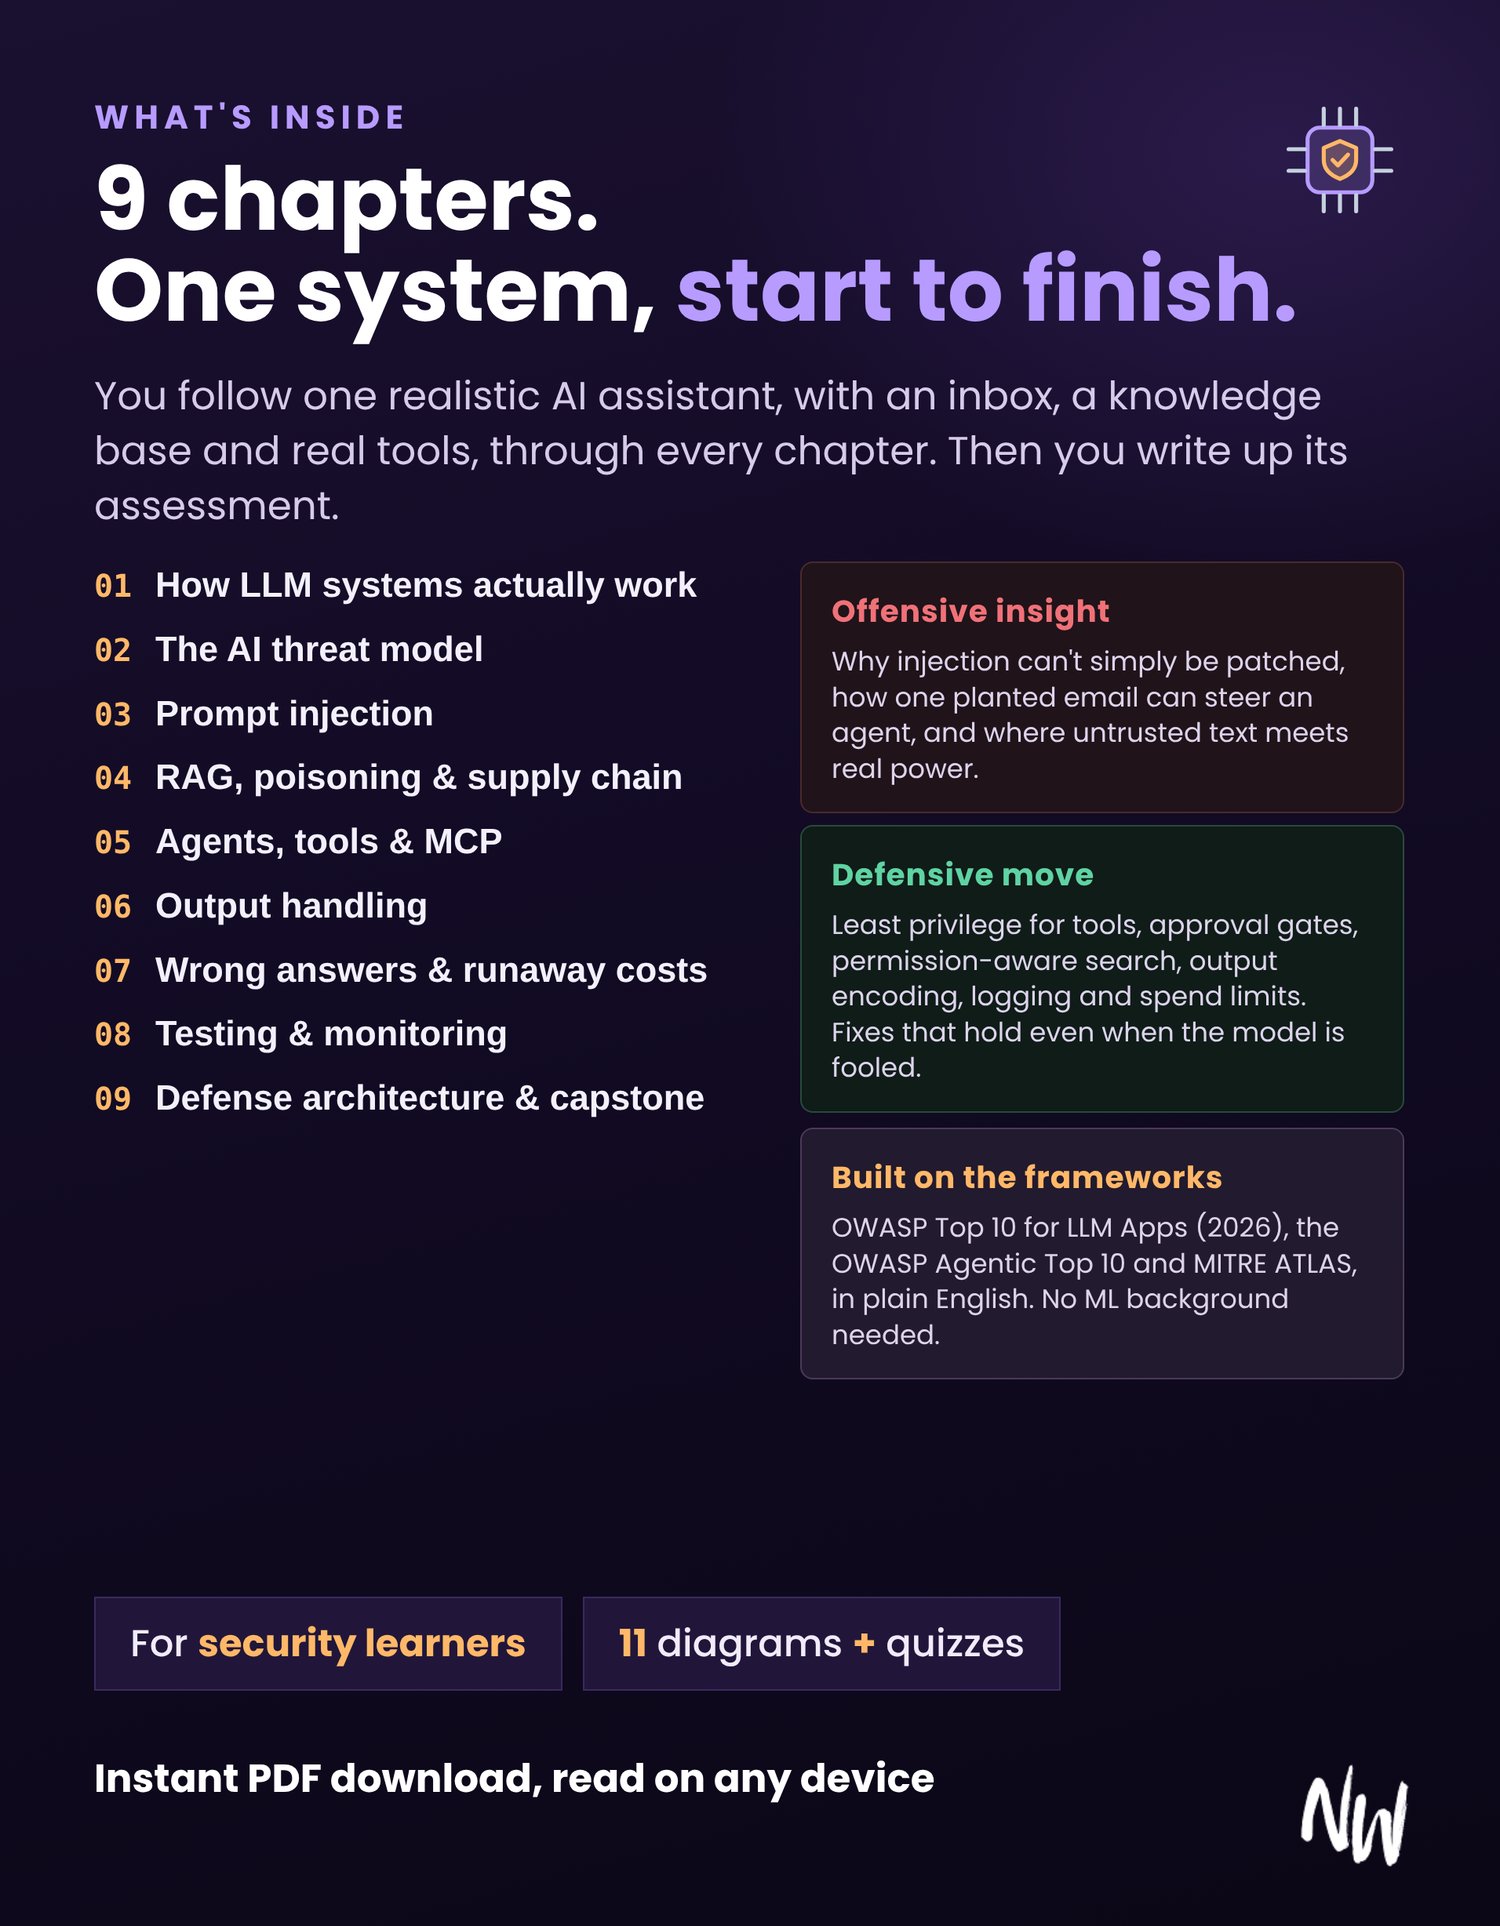
You follow one realistic system, Kestrel Assist, all the way through. It’s a freight company’s support assistant that reads an inbox, searches a knowledge base and can send emails and issue refunds. Every chapter looks at it through a new lens. By the end you’ve assessed it from start to finish and written up the findings the way a professional would.
What’s inside:
- How LLM systems actually work (context, RAG, agents)
- A repeatable threat model for any AI system
- Prompt injection: direct, indirect and hidden
- RAG, poisoning and the AI supply chain
- Agents, tools, MCP and excessive agency
- Output handling, where classic web security comes back
- Wrong answers, liability and runaway costs
- Testing and monitoring, with authorization and ethics first
- Defense architecture and a complete sample assessment report
Every topic is taught from both sides: how the weakness is abused, and how it is caught and contained. Each chapter ends with a review quiz, and the full answers are at the back of the book.
It’s built on the OWASP Top 10 for LLM Applications (2026), the OWASP Agentic Top 10 and MITRE ATLAS, translated into plain English. No machine learning background needed.
Who it’s for: cybersecurity learners and early-career practitioners, plus developers building AI features.
Format: PDF, 49 pages, instant download.
This book is for understanding and defending AI systems you own or are authorized to test.