
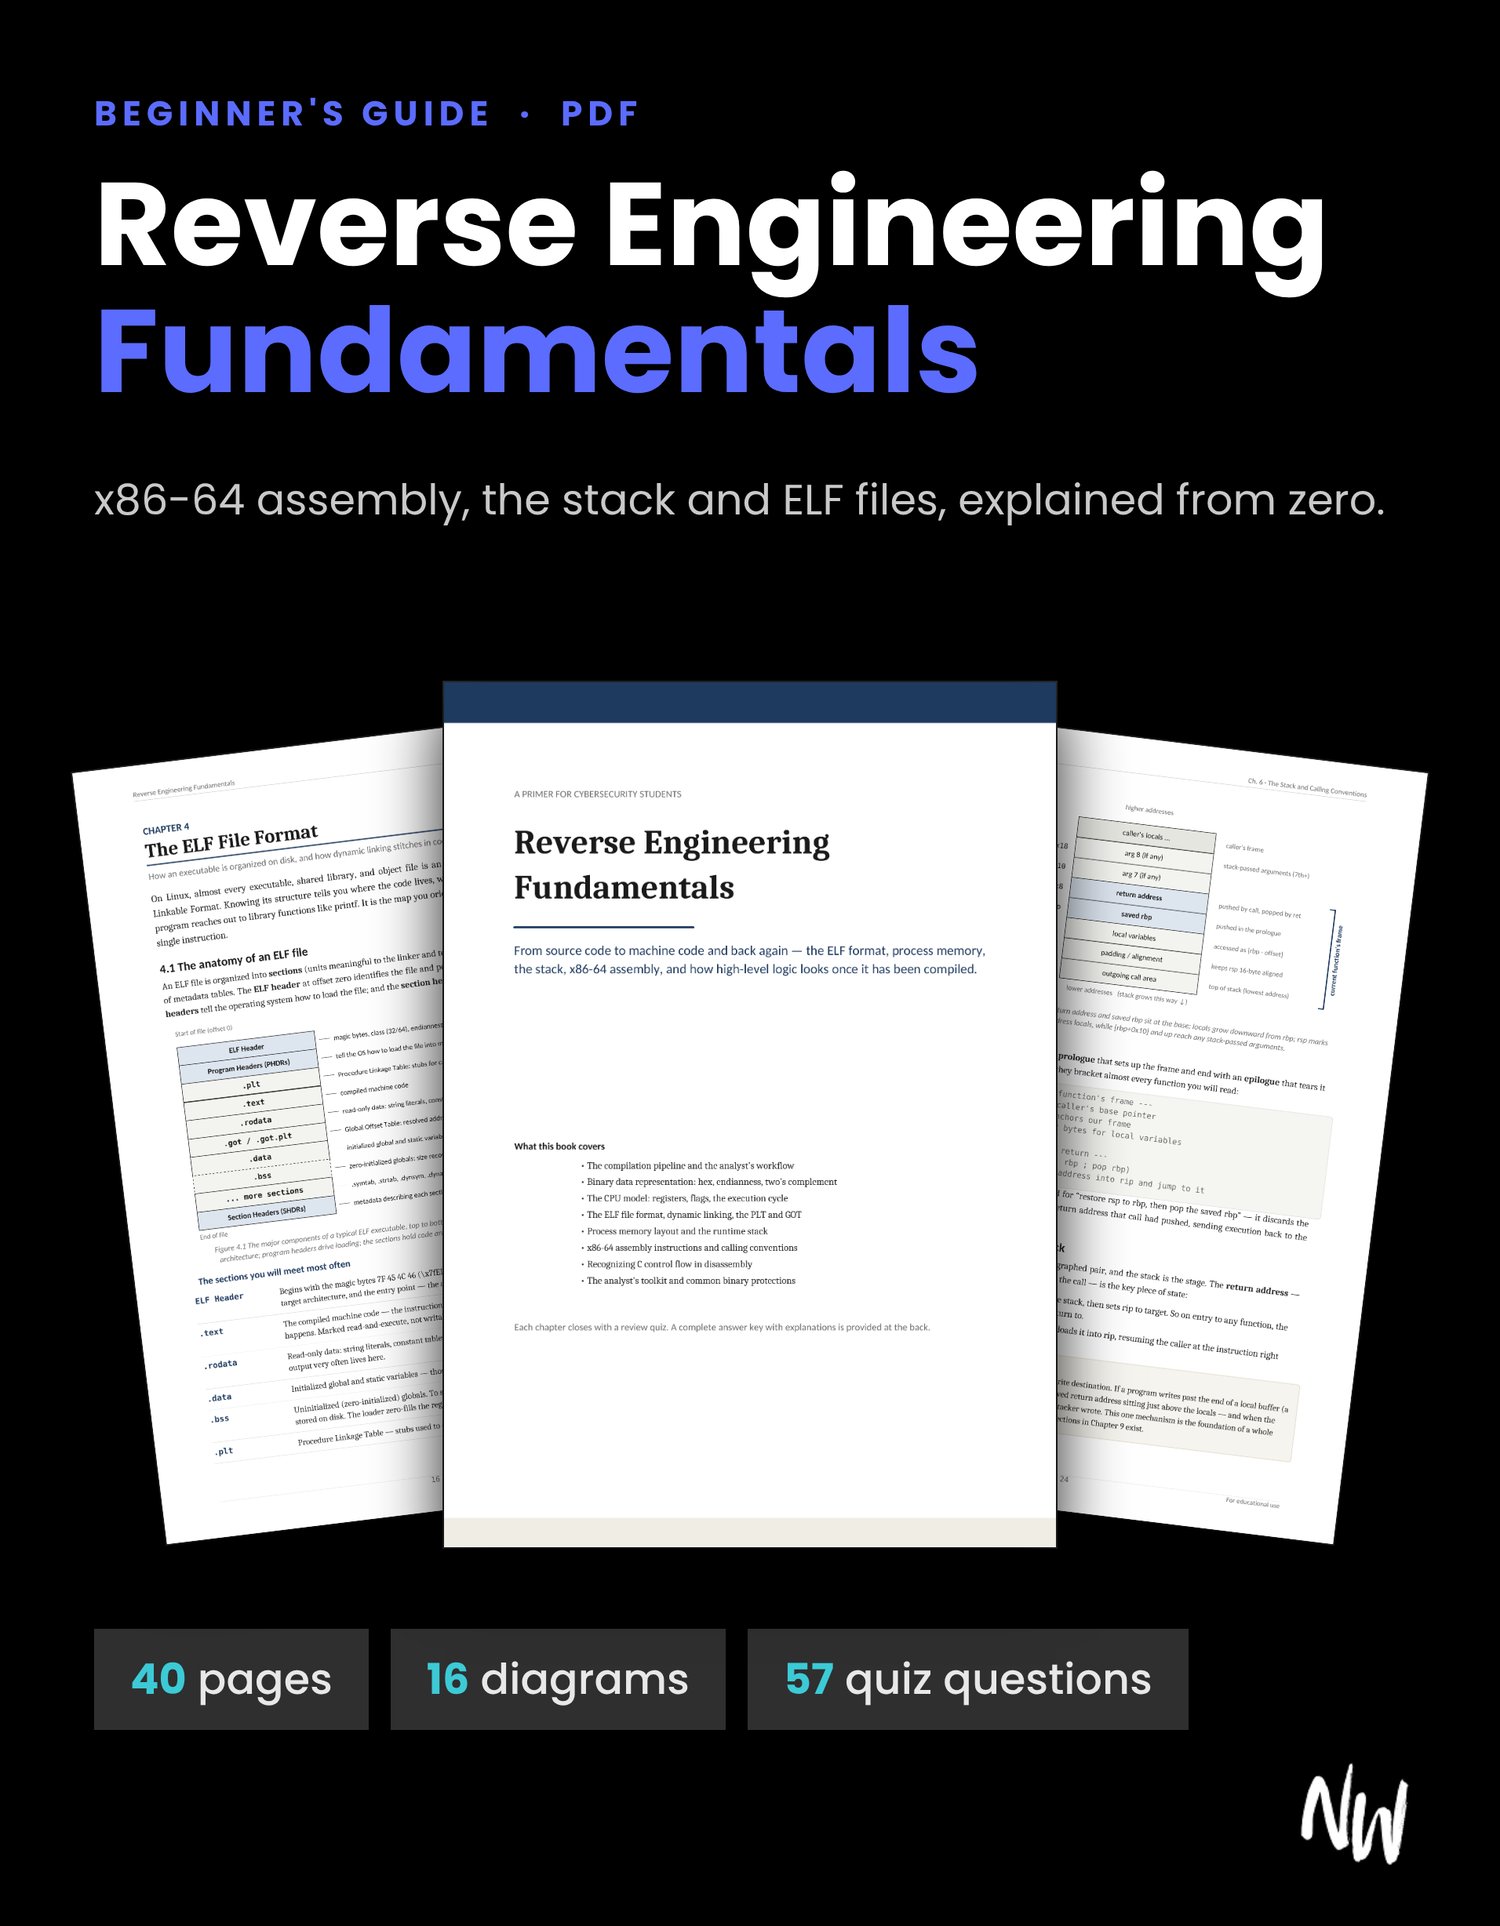
Reverse Engineering Fundamentals: A Beginner’s Guide to x86-64 Assembly, the Stack and ELF
On Sale
$13.99
(50% off)
$7.00
From zero to ready to get into reverse engineering with the fundamentals and knowledge that lets you analyze real binaries.
Reverse Engineering Fundamentals is a 40-page PDF primer for cybersecurity students, enthusiasts, and practitionners. It starts at how data is stored and ends at recognizing real control flow in compiled code. Every chapter closes with a review quiz.
What’s inside
- Reverse engineering basics: the compilation pipeline, static vs. dynamic analysis, a typical analysis workflow
- Data representation: hex, two’s complement and endianness
- The CPU: registers, flags and the execution cycle
- The ELF file format: sections vs. segments, the PLT and GOT, lazy binding
- Process memory layout: stack, heap, shared libraries, W^X and ASLR
- The stack and calling conventions: frames, call/ret, 32-bit vs. 64-bit
- x86-64 instruction reference: data movement, arithmetic, comparisons and jumps
- C to assembly: spotting if/else, loops and switch statements
- Tools and protections: Ghidra, GDB, stack canaries, NX, PIE and RELRO
Also included
- 16 diagrams: stack frames, PLT/GOT, memory map, control-flow graphs
- 9 review quizzes with 57 questions, plus a full answer key that explains every answer