
Deploy Security Automations
Incident Response Automation for n8n AI Triage, Ticket & Notify
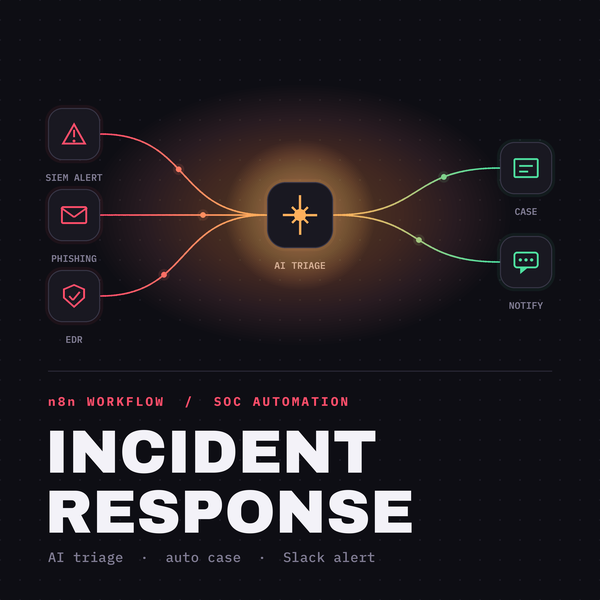
Alerts arrive from three places, get enriched and scored by an AI agent, and end up as a single ticket with a Slack ping.
What it does:
Three ways in: Creates webhook for SIEM alerts, a mailbox watcher for user-reported phishing, and a webhook for EDR detections. Each one gets normalized into the same shape, so everything downstream works no matter where the alert came from.
Deduplication: Repeat alerts for the same indicator get skipped instead of spawning a fifth ticket for the same thing.
AI triage agent: Reads the alert, calls VirusTotal (IP and file hash) and AbuseIPDB for reputation data, and returns a structured verdict: severity, what it thinks is happening, and a recommended next step. The output is then parsed to a fixed format, so it drops straight into your ticket fields rather than arriving as a paragraph of prose.
Case creation: opens a Jira issue with the enriched details attached.
Notification: posts to your SOC Slack channel with the verdict and a link to the case.
What you get:
- The workflow JSON, ready to import into n8n
- Setup notes covering credentials, webhook URLs, and where to point your SIEM/EDR
- The triage prompt, so you can tune severity thresholds to your environment