
ISO 27701 Privacy Management System Toolkit with GDPR and US State Law Annexes
FULL DESCRIPTION
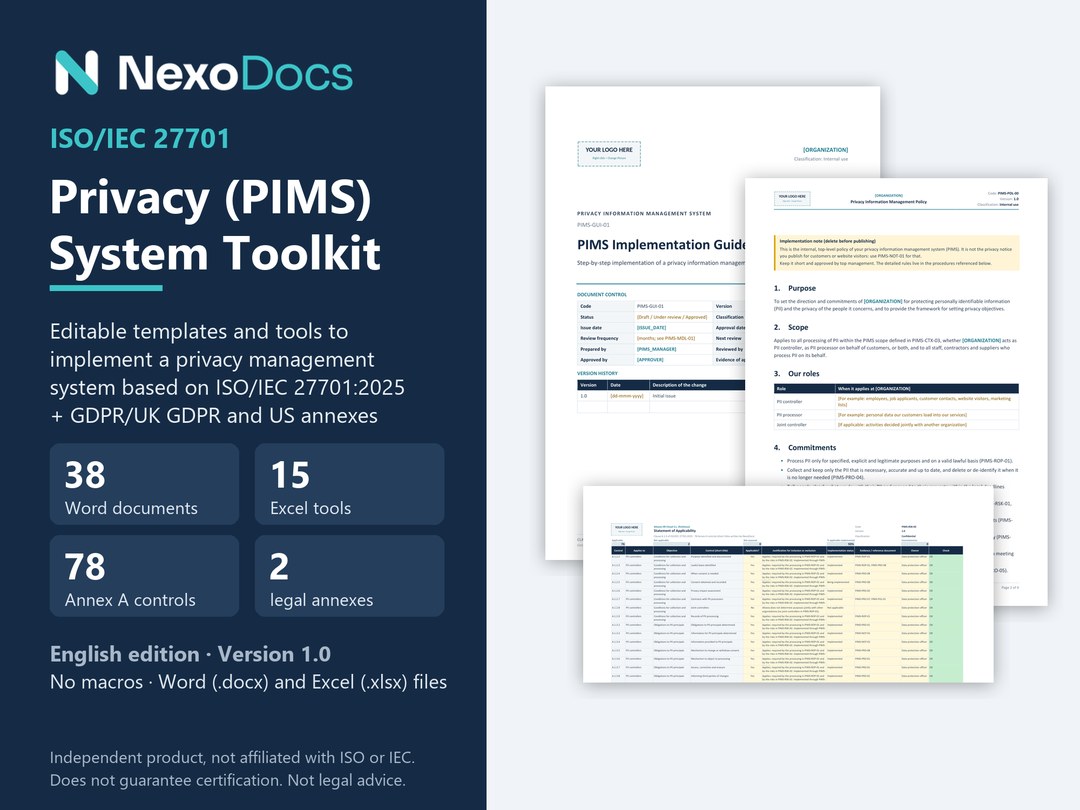
Do you need to implement a privacy information management system based on ISO/IEC 27701:2025 without starting from a blank page? The 2025 edition turned ISO/IEC 27701 into a standalone management system standard: you can implement it on its own or alongside ISO/IEC 27001. The NexoDocs Privacy Management System Toolkit brings together, in English, the templates and tools for the whole cycle: gap self-assessment, context and PII roles (controller and processor), legal requirements, scope, privacy policy, privacy risk assessment and treatment, Statement of Applicability for the Annex A controls, records of processing, privacy notice, data subject requests, privacy impact assessment (DPIA), breach response, retention and disposal, international transfers, privacy by design, processors and suppliers, lawful basis and consent, awareness, indicators, internal audit, management review and improvement.
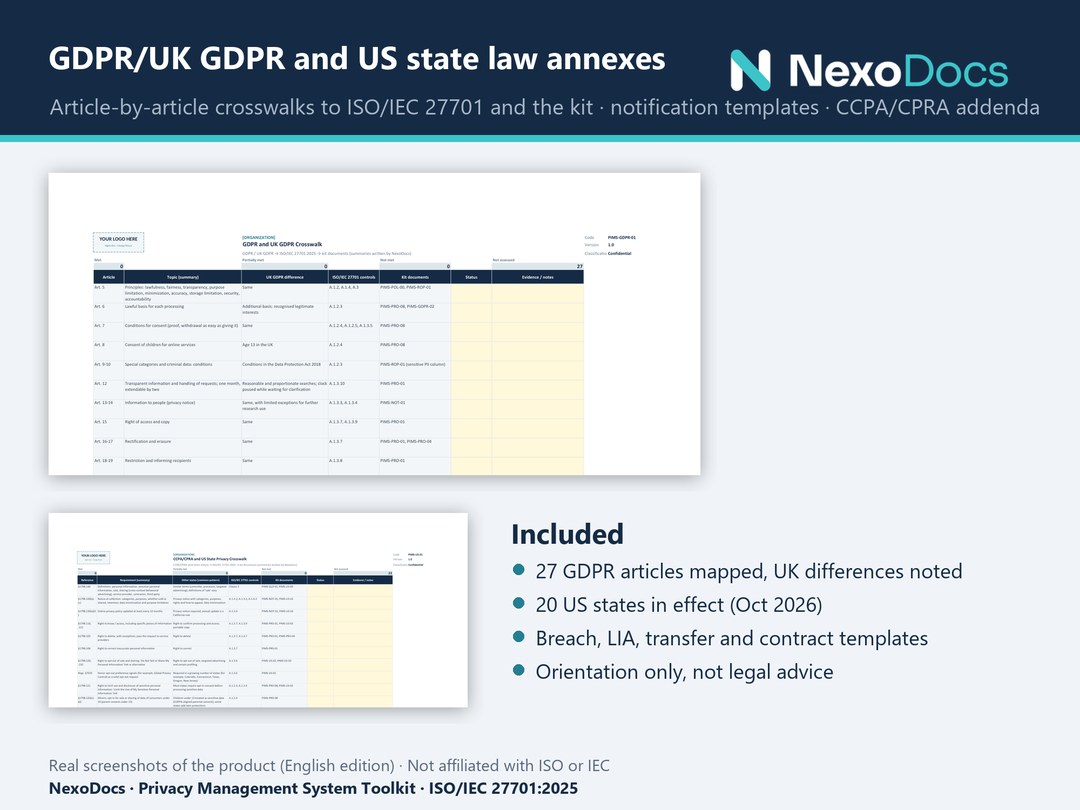
This English edition also includes two legal annexes: GDPR and UK GDPR (article-by-article crosswalk, legitimate interests assessment, breach notification templates for articles 33 and 34, DPO and representative assessment, transfer risk assessment and the UK complaints procedure introduced by the Data (Use and Access) Act 2025) and US state privacy laws (the 20 states with a comprehensive law in effect as of October 2026, CCPA/CPRA crosswalk, privacy notice addendum with opt-out links and Global Privacy Control, consumer request and appeal procedure, and service provider/processor contract addendum).
Every Word document has a cover with document control, a replaceable logo, a header and footer with classification, an implementation note explaining what to adapt, the decisions your organization must take before approval and what the auditor usually checks. The Excel tools calculate risk levels, consistency checks, deadlines and progress automatically; formulas are protected without a password and inputs are guided by drop-down lists. Completed examples show the templates adapted to a fictitious HR software company (Altavia HR Cloud) that acts as both controller and processor.
WHAT IS INCLUDED
- 61 files: 38 Word documents, 15 Excel tools, 6 PDF guides and 2 text files.
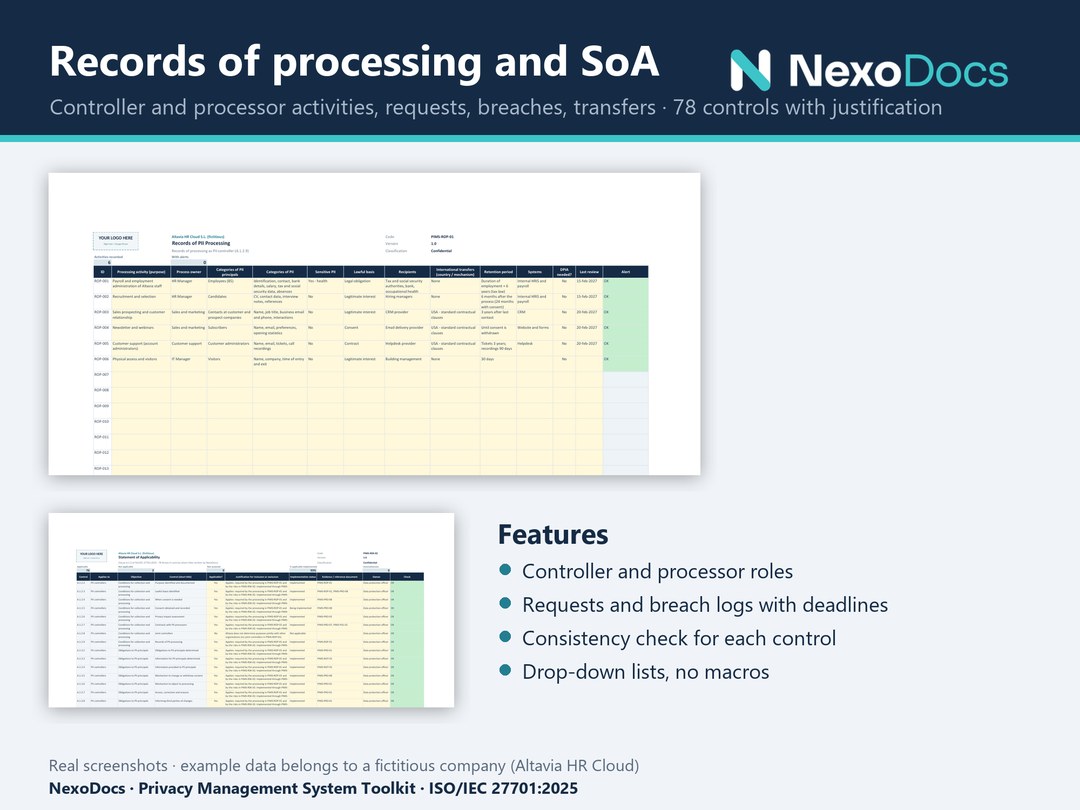
- Statement of Applicability for the 78 Annex A controls of ISO/IEC 27701:2025, with justification and consistency checks.
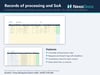
- Records of processing as controller and as processor, plus logs for requests, breaches, transfers, disclosures and processors.
- Privacy risk register with heat map, privacy objectives and indicators.
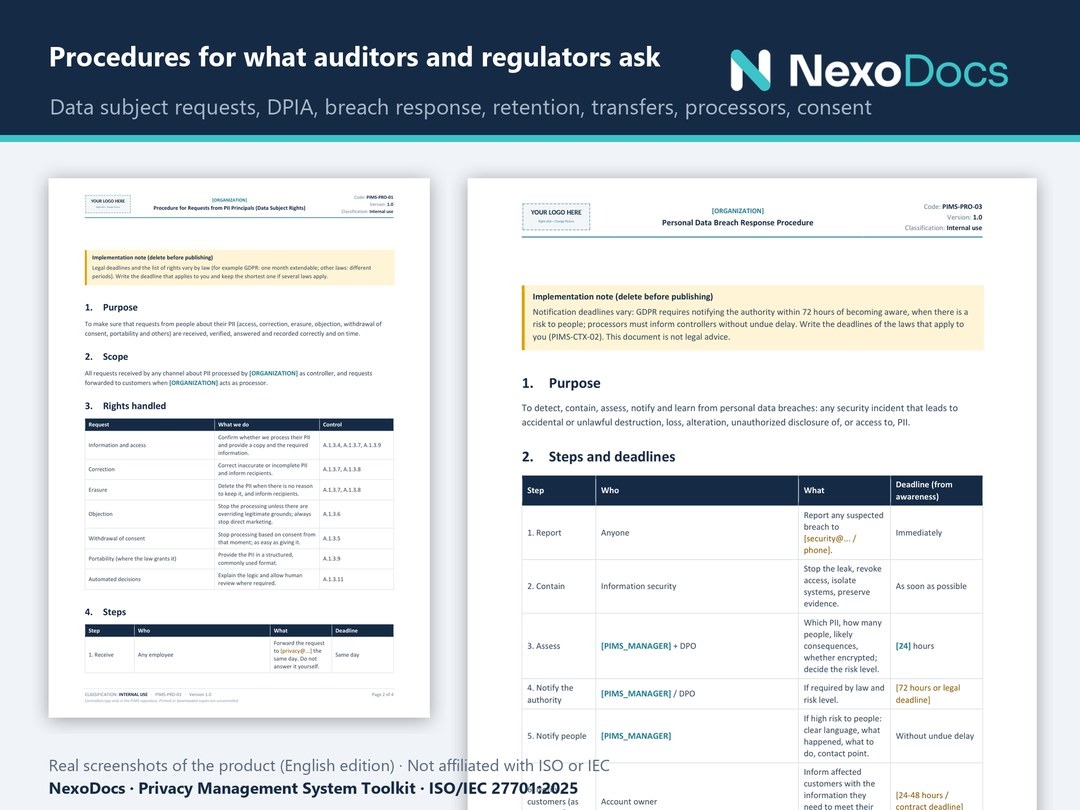
- Procedures for data subject requests, DPIA, breach response, retention, transfers, privacy by design, processors and consent.
- Data processing agreement template and processor obligations policy.
- Cross-mapping with the NexoDocs ISO/IEC 27001 toolkit, for an integrated ISMS + PIMS.
- Implementation guide, master index with links and a case study.
WHO IT IS FOR
Privacy and data protection leads, DPOs, compliance and information security managers in SaaS companies, service providers and any organization that processes personal data as controller or processor, and consultants who implement ISO/IEC 27701.
DELIVERY AND COMPATIBILITY
Instant download of one ZIP file (about 2.5 MB). No macros. Tested in Microsoft Word and Excel for Windows (Microsoft 365). License for one organization: use with your own staff and contractors; resale and distribution to third parties are not allowed.
NOTICES
Independent product, not affiliated with ISO or IEC. It does not reproduce the text of the standard, which must be purchased separately, and it does not guarantee certification, which depends on your implementation and on the certification body. The legal annexes are orientation written by NexoDocs, cite laws by article or section number only and are not legal advice; legal status checked in October 2026.
AI NOTICE: content created with substantial AI assistance (Claude) and checked with automated tests in Microsoft Word and Excel.
Questions: hola@nexodocs.com · nexodocs.com