Practical Cyber-Risk & GRC Resources for Security Leaders
Board-ready templates, reporting systems and practical tools designed to help cybersecurity and GRC professionals turn complex risk data into clearer executive decisions.

Board-ready templates, reporting systems and practical tools designed to help cybersecurity and GRC professionals turn complex risk data into clearer executive decisions.
Build a repeatable, board-ready cybersecurity reporting process without starting every quarter from scratch.
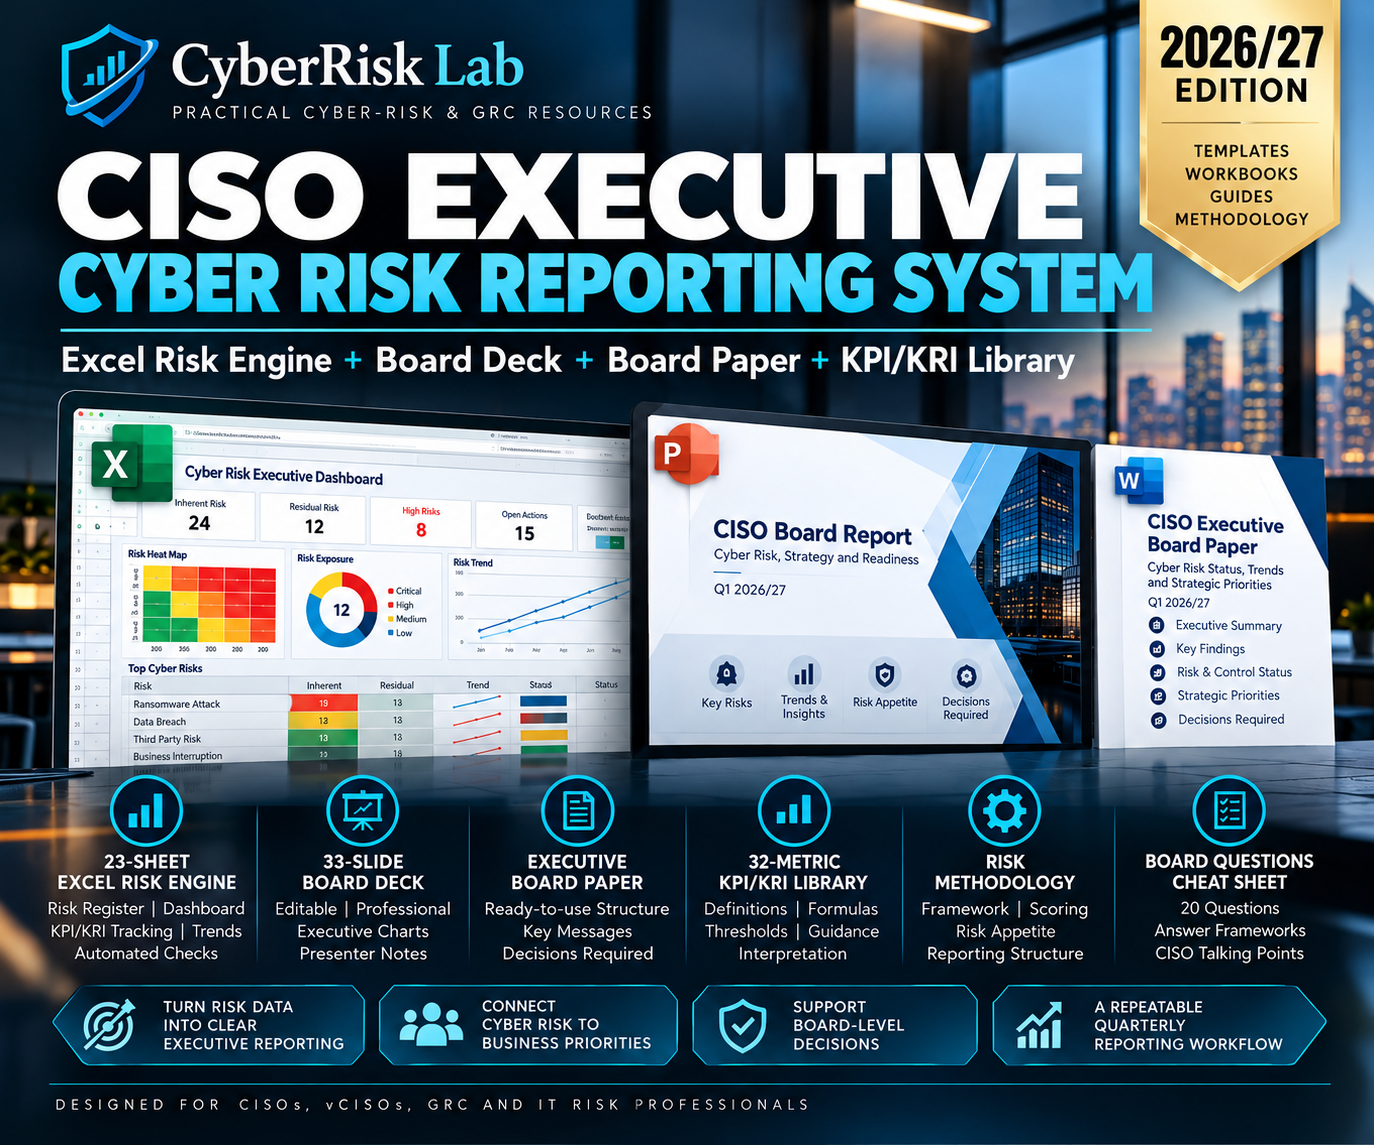
The CISO Executive Cyber Risk Reporting System is a professional digital toolkit designed for CISOs, vCISOs, Security Managers, GRC Managers, IT Risk professionals and cybersecurity consultants who need to turn cyber-risk data into clear executive reporting and board decisions.
✓ Digital product — instant download
✓ No subscription or recurring fee
✓ No macros in the Excel workbook
✓ Demo + blank working versions included
✓ Designed for Microsoft Excel, PowerPoint and Word
✓ 2026/27 Edition · Version 1.1
📊 Excel Cyber-Risk Reporting Engine
📑 CISO Board Reporting Pack
📚 Methodology & Reporting Library
✓ Present cyber risk in business language
✓ Connect risks to KPIs, KRIs and risk appetite
✓ Explain what is improving or deteriorating
✓ Turn technical metrics into management decisions
✓ Prepare clearer board-level funding and risk decisions
✓ Create a repeatable quarterly reporting workflow
CISOs · vCISOs · Security Managers · GRC Managers · IT Risk Managers · Cybersecurity Consultants · Risk & Audit Professionals
One reporting system
Risk, KPI/KRI, incidents, remediation, suppliers and controls in one workflow.
Board-ready output
The workbook feeds a structured board deck and executive paper.
Decision-focused
Designed to connect technical risk signals to management action and funding decisions.
Demo + blank versions
See a complete worked example, then build your own reporting cycle.
Built-in data-quality checks
40 automated checks help identify missing, stale or inconsistent reporting inputs.
2026/27 Edition · Version 1.1
Launch price: $59.99
Regular price: $79.99
Demo data is fictional. Thresholds, scoring, risk appetite and other methodology elements should be calibrated to the organisation's context.
CyberRisk Lab
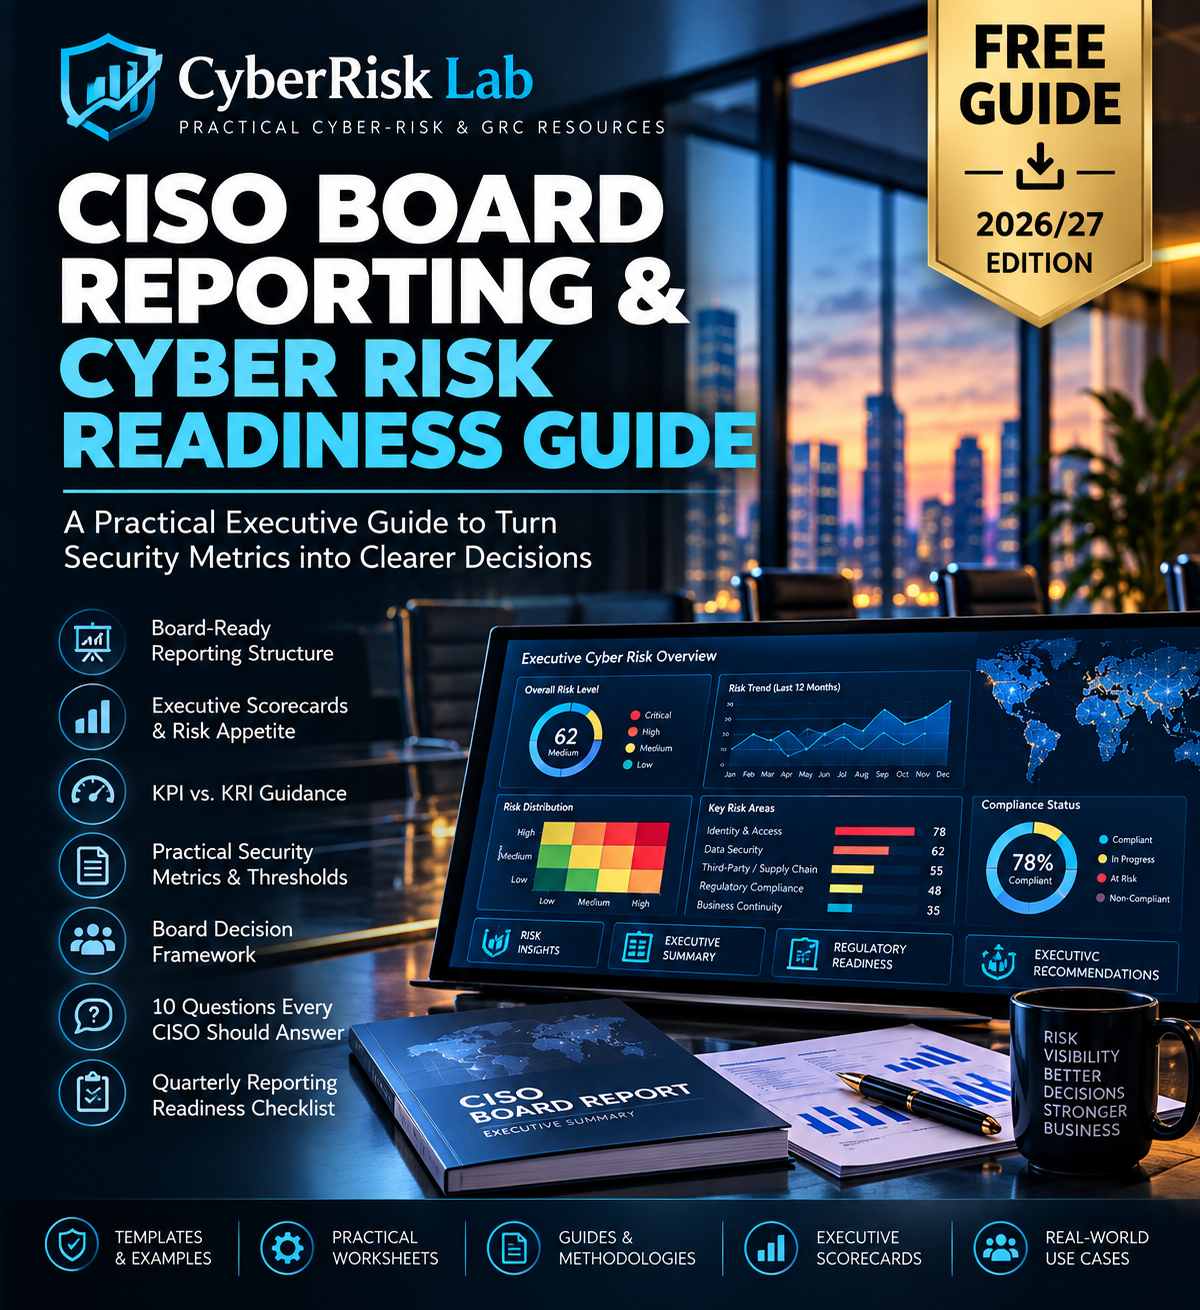
A practical executive guide for Cybersecurity and GRC professionals looking to improve board reporting, cyber-risk visibility and security decision-making.
Inside the guide:
• Board-ready cyber-risk reporting structure
• Executive scorecard and risk appetite framework
• KPI vs. KRI guidance
• Practical security metrics and thresholds
• Board decision framework
• 10 questions every CISO should be ready to answer
• Quarterly cyber-risk reporting readiness checklist