Security programs you can defend.
Policies, procedures, workbooks and worked examples for third-party, identity, risk and AI governance. Built by practising security leaders, ready to adopt this week.

Policies, procedures, workbooks and worked examples for third-party, identity, risk and AI governance. Built by practising security leaders, ready to adopt this week.
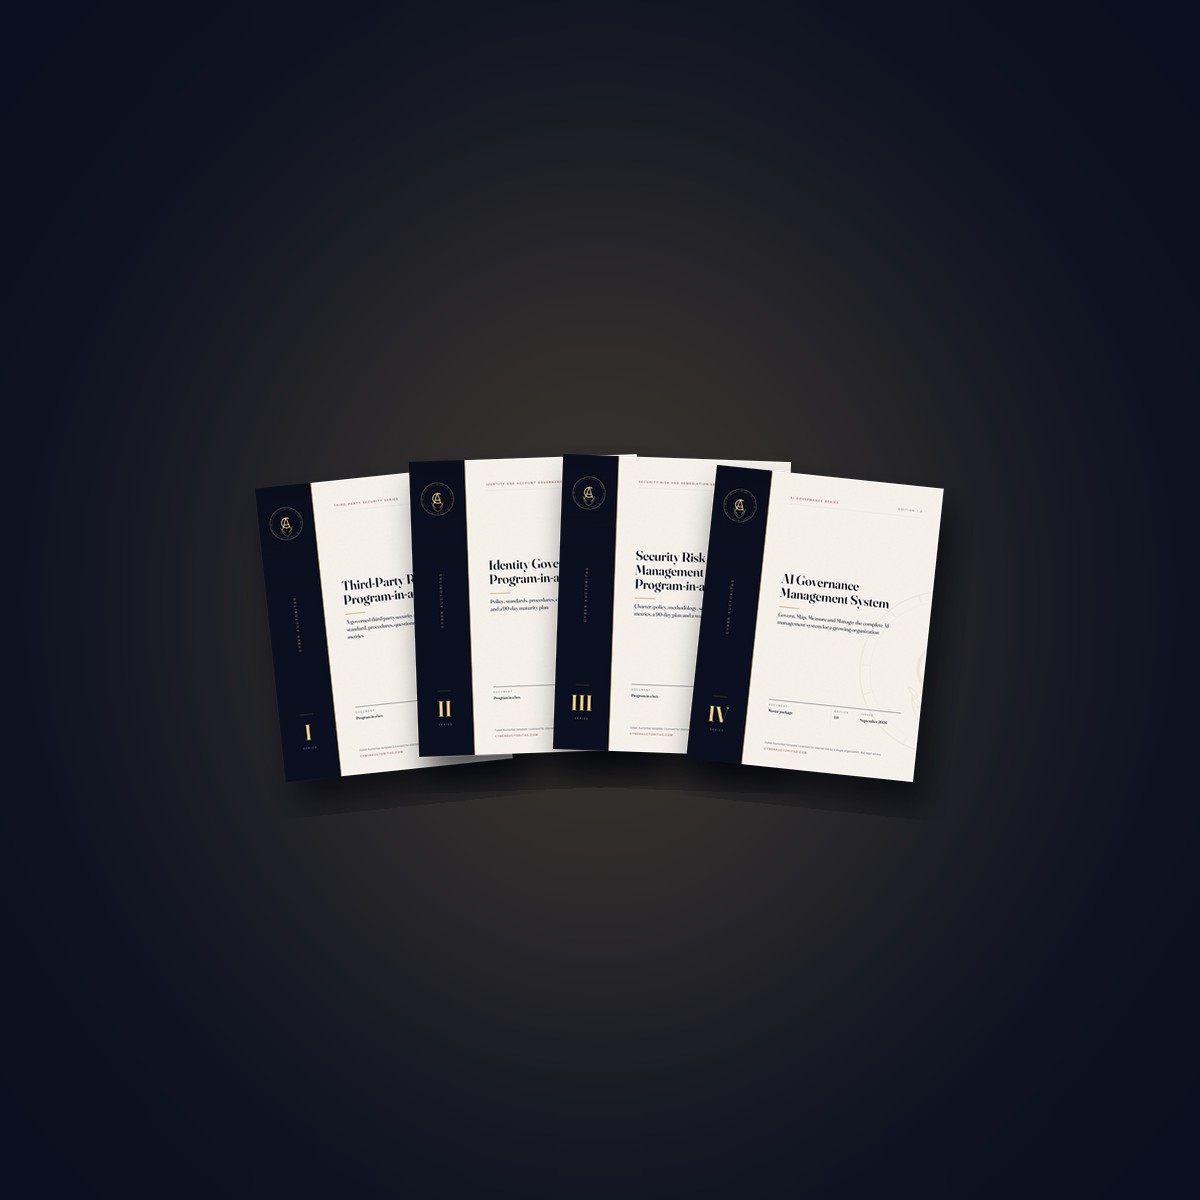
Most growing organizations know what a security program should contain. What they lack is the weeks it takes to write the policy, design the workbook, work out the scoring and draft the forms, and the months it takes to learn which parts hold up when an auditor, an insurer or an incident tests them.
These programs are that work, done by practitioners who have built and run security programs across financial services, the defense industrial base, higher education, manufacturing and member associations. Every document is written to be adopted, not admired.
A self-scoring maturity check: a PDF guide and an Excel scorecard. Ten to twenty minutes, and it tells you the first move for your weakest area.
The first working artifacts: a register or inventory, the core forms and a short guide to put them to work.
The full operating workbook with every calculation, worked sample data, the implementation guide and the complete form set. List price $49.
Charter, policy, standards, procedures, metrics and the implementation plan: the whole program, ready for approval. List $149; the AI Governance Program is $99.
Every procedure has been run, every threshold argued over with a real leadership team, and every form exists because an auditor or insurer asked for the evidence it produces.
The workbooks ship with realistic sample data, and the larger programs include a fictional organization months into its program, so you can see the whole system working first.
Each series maps to the frameworks your customers and auditors cite, including NIST CSF 2.0, CIS Controls v8.1, ISO/IEC 27001:2022 and the NIST AI RMF. Nothing here claims to certify you.
Word, Excel and PDF that work in Microsoft Office 2010 and later and convert cleanly to Google Docs and Sheets. No subscription and no platform to log into.
Cyber Auctoritas is an independent security practice built by senior practitioners. We build and run security programs for organizations that have outgrown spreadsheets but do not need an enterprise GRC suite, and we hold them to one test: whether they hold up on a bad day, not whether they pass on a good one. The same methods behind these programs are delivered as advisory work and on the AtlasSec platform.
No. Microsoft Excel 2010 or later and Word, or Google Sheets and Docs. No macros, add-ins or installs.
The standard licence covers one organization. Consultants, vCISOs and managed service providers need a practitioner licence; see the Licensing page.
They give you a working program aligned to the major frameworks and the evidence to show it operates. Compliance is a judgment your auditor makes, and nobody selling templates can make it for you.
A short working note on running a security program: a technique, a template change, a finding from the field. No sales sequence. Unsubscribe in one click.