Your Cart
Loading

You need a security program, and you are starting from nothing.

A customer's security review asks which framework you follow. An insurer wants proof of your controls. The board asks how secure you are, and nobody can answer with more than a feeling.


A framework gives the program its shape, but a framework is a list of requirements, not a program. Turning it into one is the work these packages have already done.
Coverage ring showing the five parts of the problem, all still open.

The problem has five parts.

Starting a program is not one problem. It is five, and buying a framework document solves none of them.


1. You do not know where you stand. No honest, item-by-item baseline against any framework.


2. You do not know what to fix first. Every gap looks equally urgent, so nothing gets done.


3. Your policies are missing or say nothing. No written rules, or rules copied from somewhere else that nobody follows.


4. You cannot prove what you claim. The policy says one thing, the organization does another, and there is no evidence of either.


5. Nobody governs it. No program documents, metrics or plan, and nothing an assessor, a customer or a board can examine.

Three frameworks. Pick the one your buyers name.

NIST CSF 2.0 if you need to explain your program to a board, an examiner or an insurer. It is the common language they now use, and version 2.0 added the GOVERN function, where most organizations find their largest gaps.


CIS Controls v8.1 if you need to know which defensive actions to take, and in what order. Implementation Group 1 is the baseline insurers and customers increasingly expect.


ISO 27001 if customers or tenders require a certificate. It fails most often not on technical controls but on the management system around them.


Not sure? Start with CIS Controls if your problem is what to do, and NIST CSF if your problem is how to report it. The Toolkit and Complete editions include a crosswalk to the other two, so evidence is collected once.

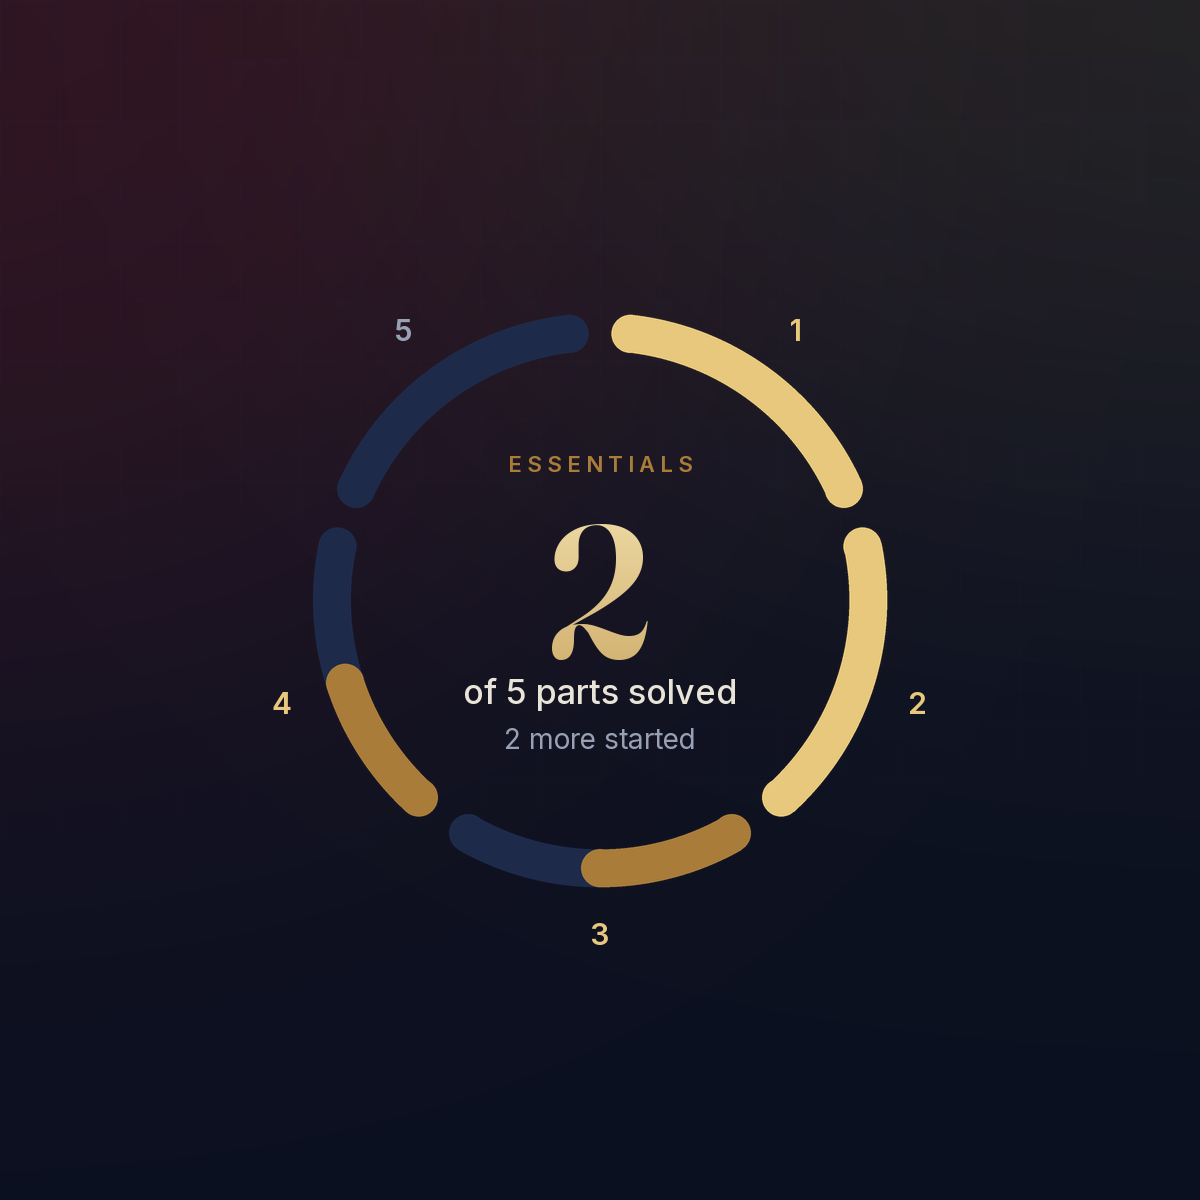
Coverage ring: Essentials solves parts 1 and 2 and starts parts 3 and 4.

Know where you stand, and what to fix first.

ESSENTIALS, $49 FOR EACH FRAMEWORK


NIST CSF 2.0 Essentials, CIS Controls v8.1 Essentials, ISO 27001 Essentials


Solves part 1. A self-scoring assessment covering every item in the framework on a zero to five maturity scale, with a target for each.


Solves part 2. Every gap is placed in a wave, do first, do next or do later, and the summary rolls it up into a current-versus-target chart for leadership.


Starts part 3. The three foundation policies every program starts with, Information Security, Acceptable Use and Access Control, each with its full technical procedure.


Starts part 4. Flags any level three or higher claim that has no evidence behind it. Tracking the evidence itself is in the Toolkit.


Still open: part 5. Nothing here governs the program yet.

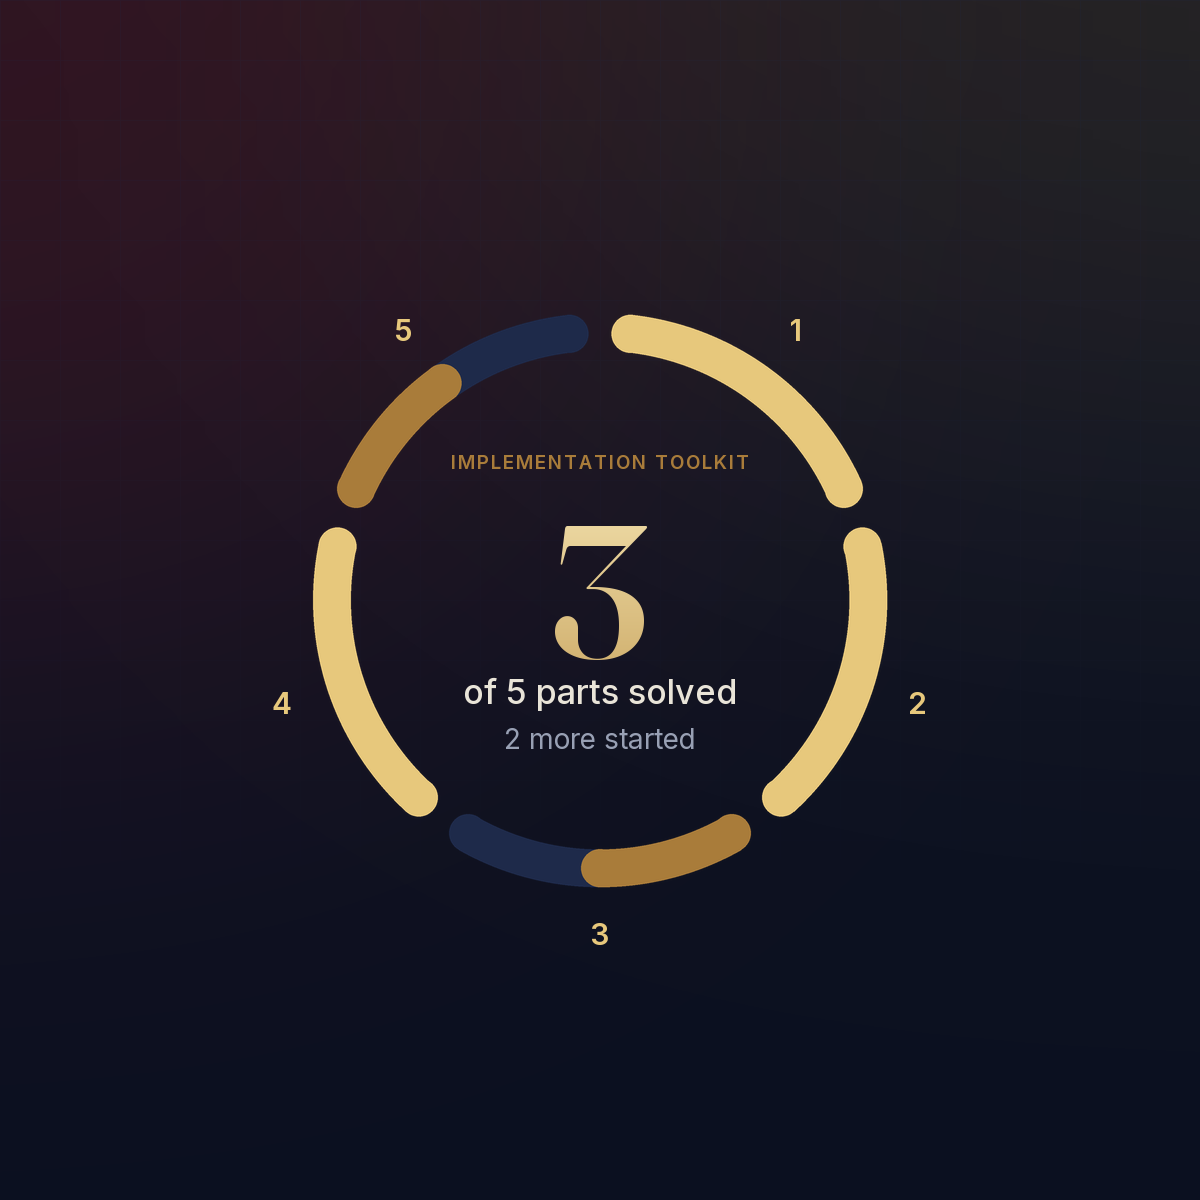
Coverage ring: the Implementation Toolkit solves parts 1, 2 and 4 and starts parts 3 and 5.

Run the program, not just the assessment.

IMPLEMENTATION TOOLKIT, $149 FOR EACH FRAMEWORK


NIST CSF 2.0 Implementation Toolkit, CIS Controls v8.1 Implementation Toolkit, ISO 27001 Implementation Toolkit


Solves parts 1 and 2, with gaps turned into initiatives on a roadmap with owners, dates and overdue flags.


Starts part 3. Eight core policies, each with its companion procedure. The full set of sixteen is in the Complete Program.


Solves part 4. Policy, practice and evidence are scored separately, and the result is capped at one level above the weakest, which is the score an auditor would give. An evidence register tracks every artifact and tells you what to refresh.


Starts part 5. A crosswalk to the other two frameworks, and for ISO 27001 a generated Statement of Applicability. There are no program documents or metrics yet.

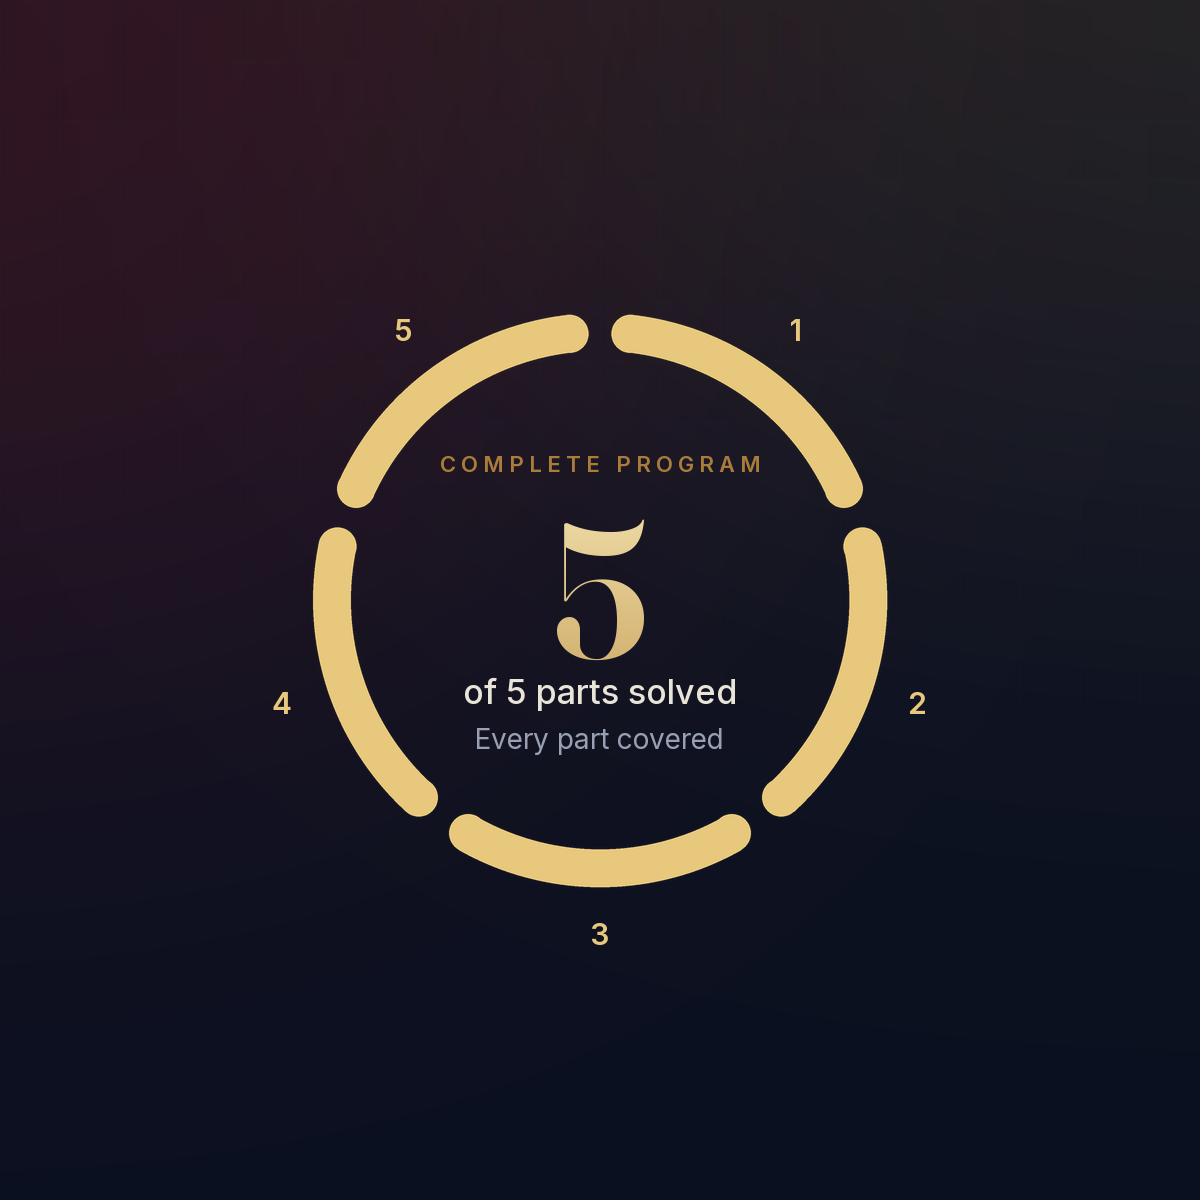
Coverage ring: the Complete Program solves all five parts.

A governed program in ninety days.

COMPLETE PROGRAM, $349 FOR EACH FRAMEWORK


NIST CSF 2.0 Complete Program, CIS Controls v8.1 Complete Program, ISO 27001 Complete Program


Solves parts 1, 2 and 4, with the program edition workbook.


Solves part 3. All sixteen policies of eight to ten pages, each tool neutral, and sixteen companion procedures that turn each one into step-by-step execution.


Solves part 5. The program documents an assessor expects, ten program metrics with a quarterly maturity history, a week-by-week 90-day plan, and a fully worked example of a program one quarter in. The ISO 27001 edition includes every mandatory ISMS document and a certification readiness checklist.


An implementation aid, not a certification. Only an accredited certification body can certify you against ISO 27001.

What no template can do for you.

Even a complete program needs someone to run it: to set the scope, chair the reviews and decide which gaps the organization will live with. If you want that person, the practice provides senior security leadership on retainer.

Choosing the right one